How to Register App in Azure Active Directory (Microsoft Entra ID)
When opting for Modern Authentication in MailsDaddy migration and backup applications, register your application in Microsoft Entra ID (Azure AD). Follow this illustrated guide with step-by-step screenshots to configure API permissions, generate your Client Secret, and assign administrator privileges.
Register the App in Microsoft Entra ID (Azure AD)
You can complete application registration via Microsoft 365 Admin Center or directly in Azure Portal (portal.azure.com).
Sign in to the Microsoft 365 Admin center using your global administrator credentials. Under the left-hand navigation sidebar, look for Admin centers and select "Identity" (Microsoft Entra ID).
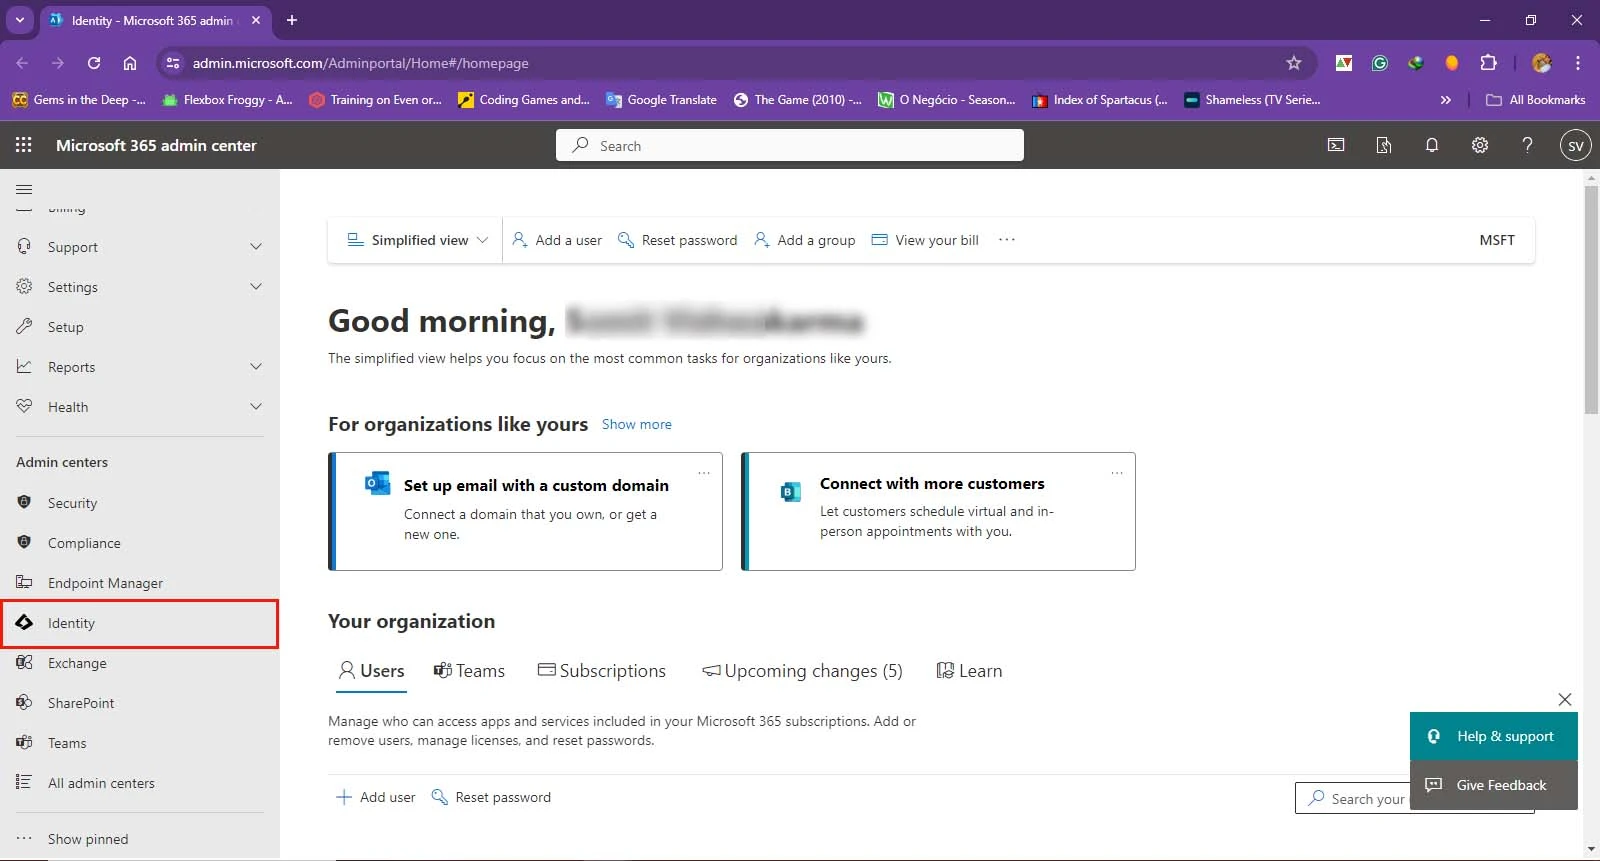
In the Microsoft Entra admin center navigation tree, expand the Applications menu and click on "App registrations".
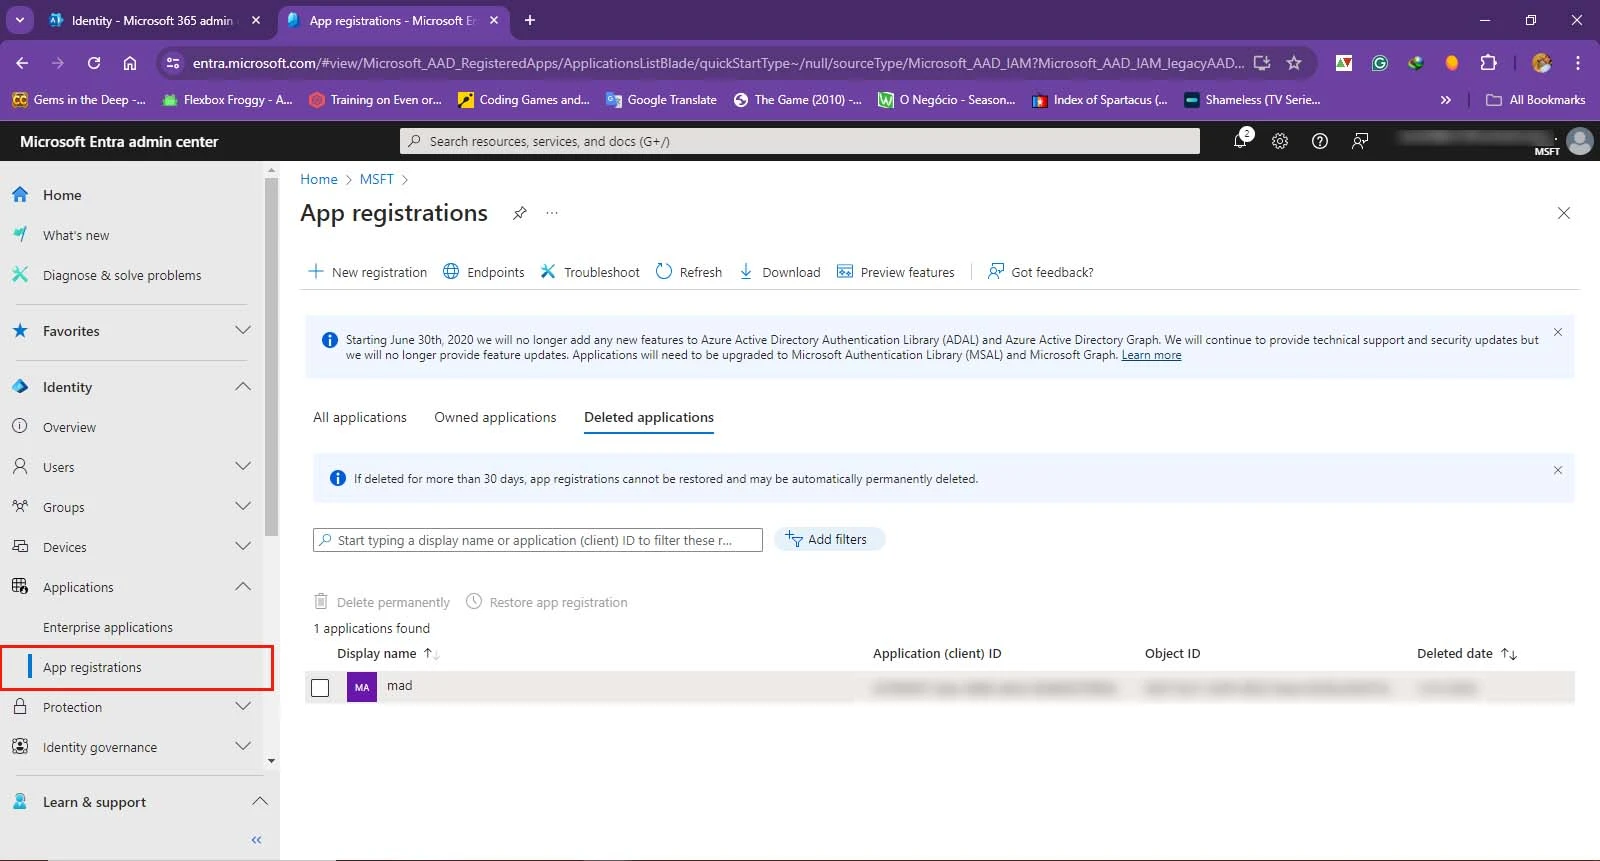
On the top toolbar of the App registrations page, click the "+ New registration" button to start creating your app.
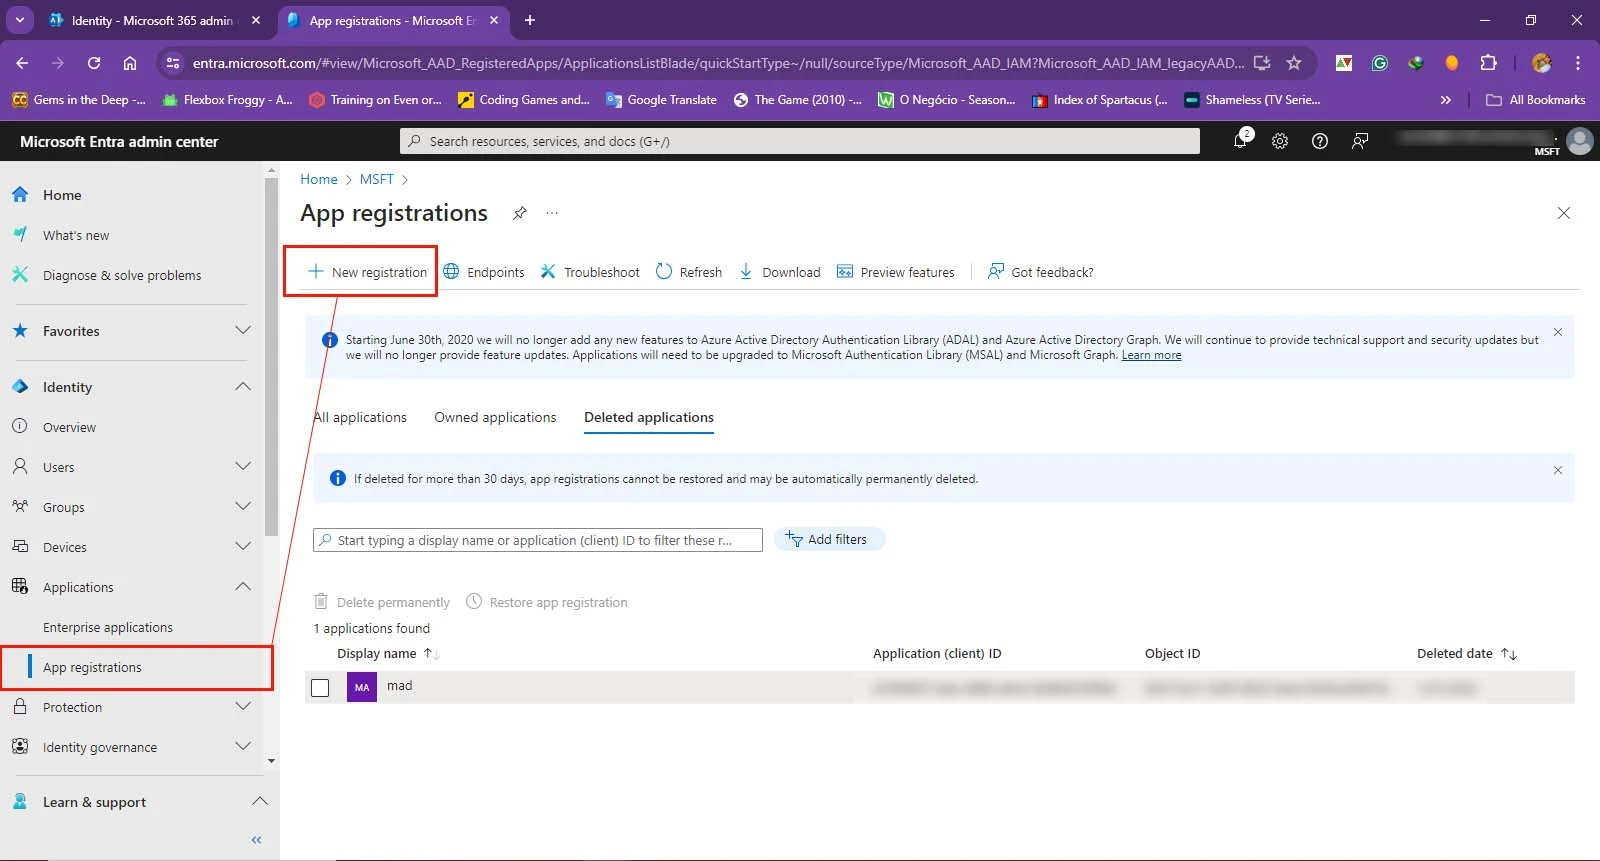
Enter an intuitive name for the app (e.g., MailsDaddy Migration App or MailsDaddy Backup). Under Supported account types, select "Accounts in this organizational directory only (Single tenant)", then click on the "Register" button at the bottom.
Add API Permissions: Office 365 (Exchange Online)
Configure application-level permissions so MailsDaddy software can access mailboxes, folders, calendars, and items.
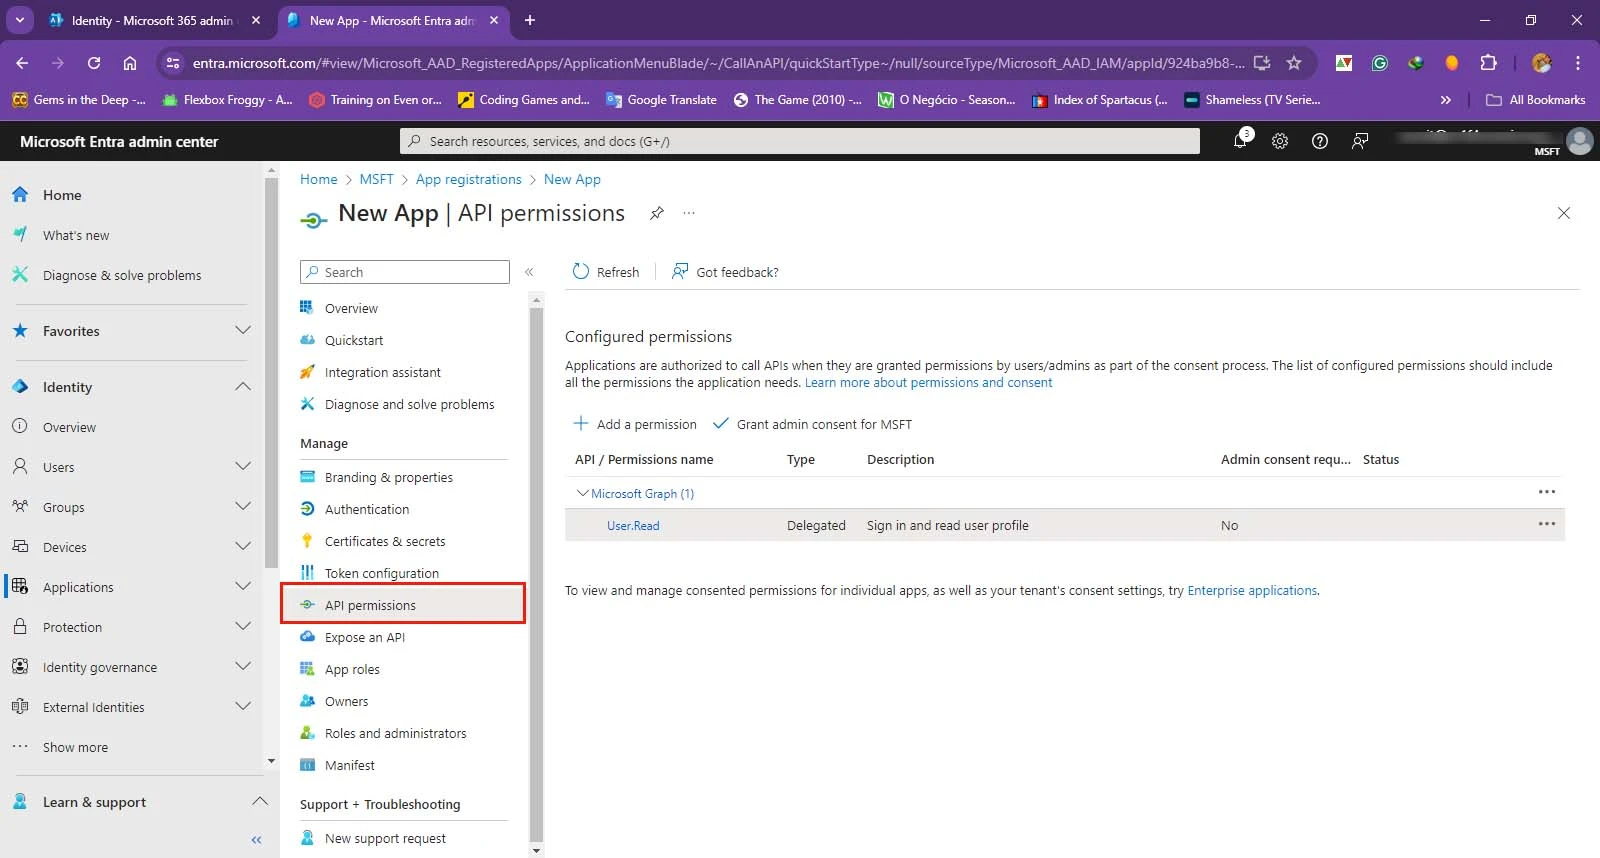
Under the Manage category in the left sidebar, click on "API permissions", then click the "+ Add a permission" button.
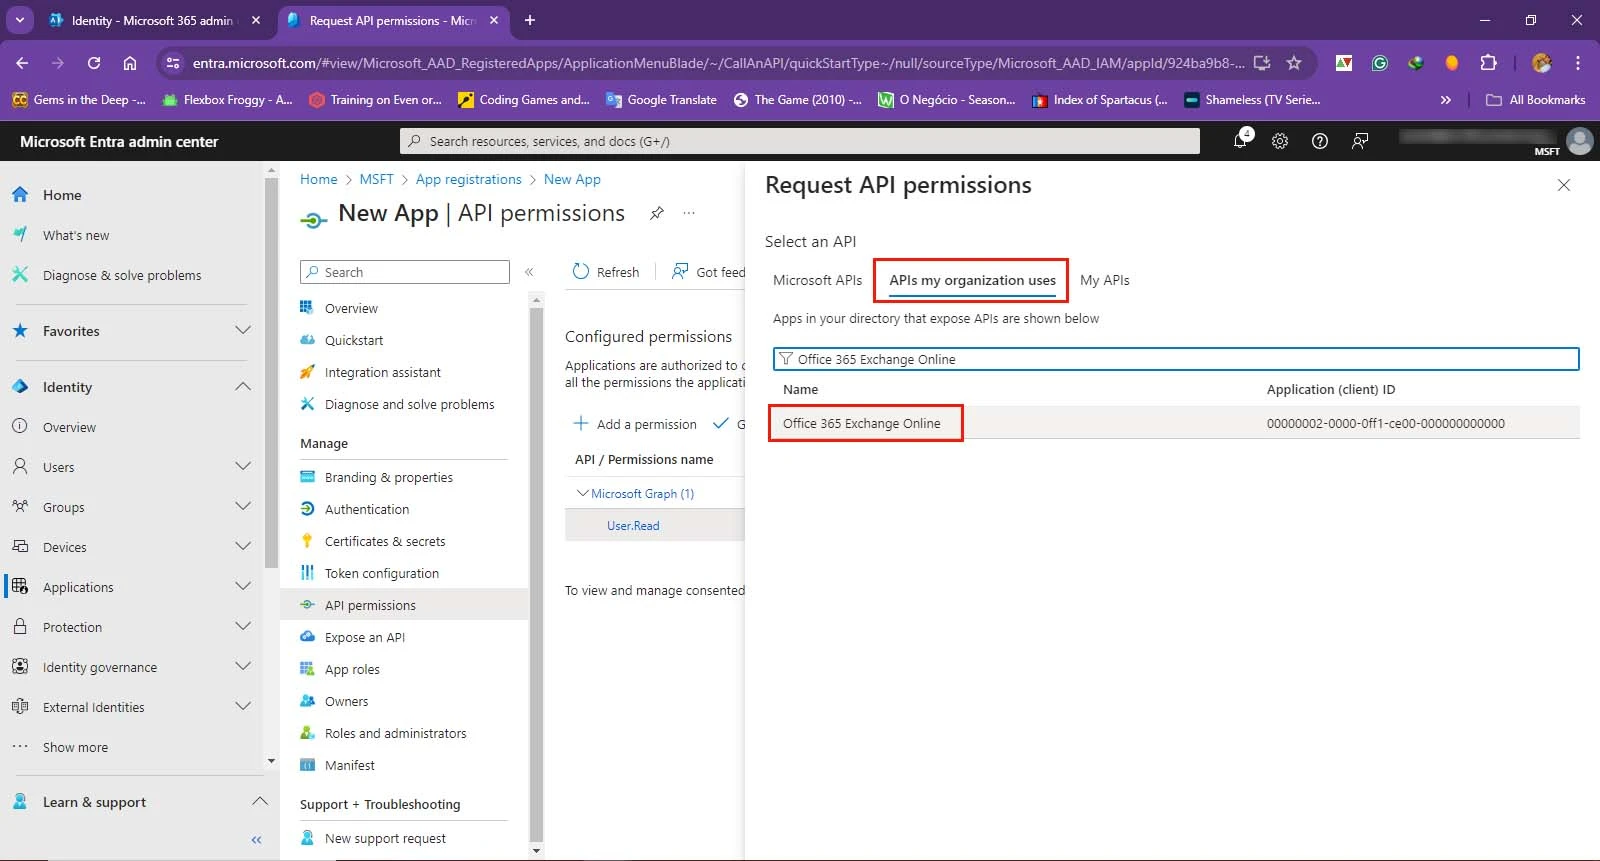
In the Request API permissions pane, click on the "APIs my organization uses" tab. Search for "Office 365 Exchange Online" and select it from the result list.
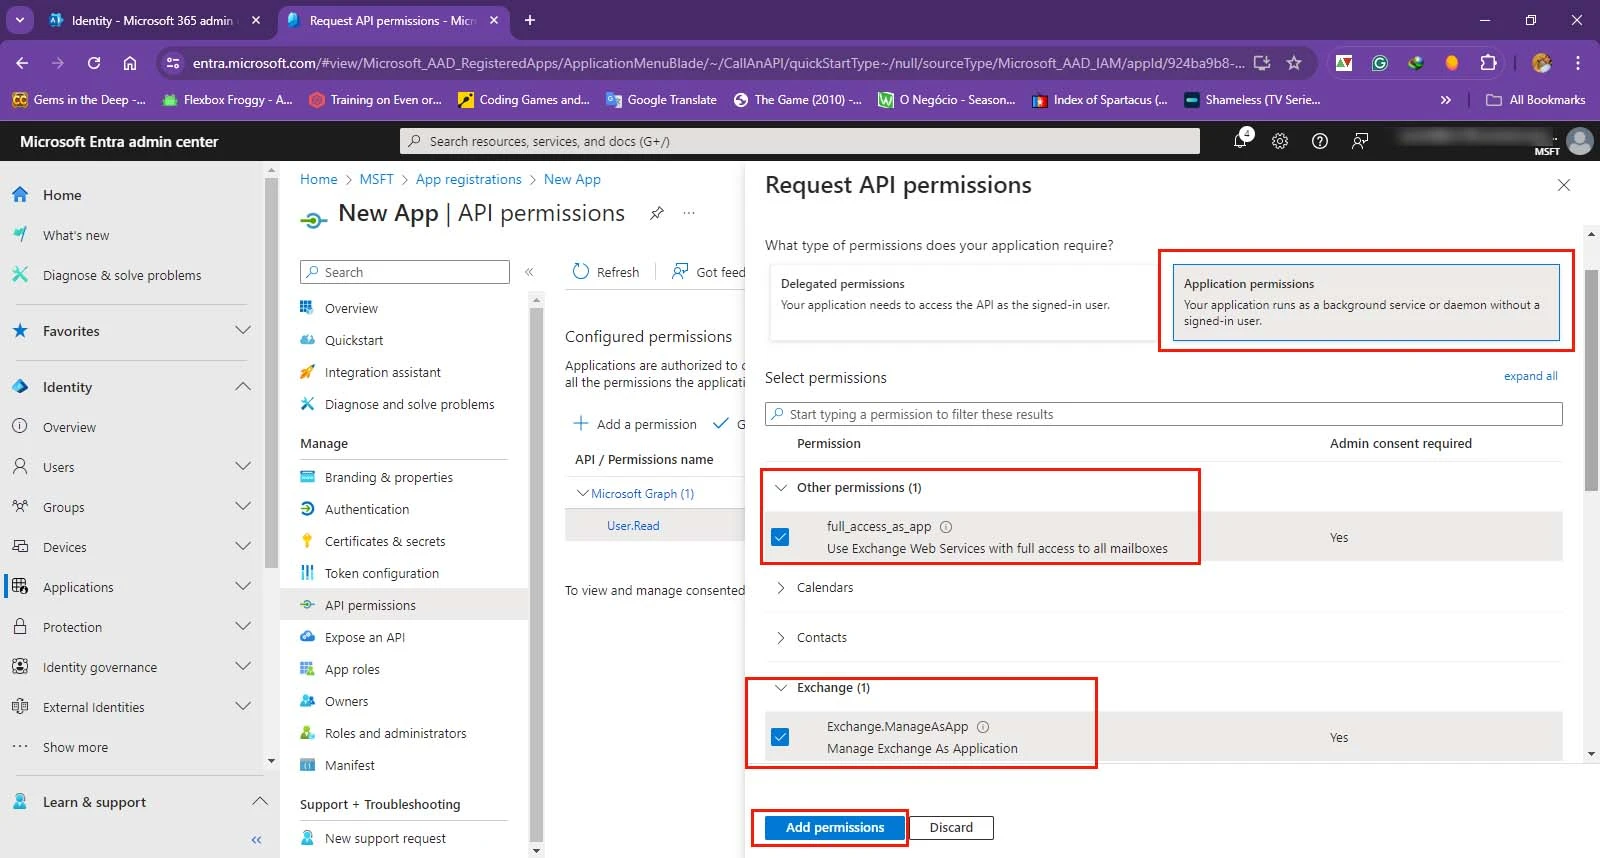
Choose "Application permissions" (runs as a background service without a signed-in user), then check the required permissions:
| Migration Type | Permission Category | Permission Name | Purpose |
|---|---|---|---|
| For Office 365 / Exchange Online | Exchange | Exchange.ManageAsApp | Manage Exchange organization as app |
| Full Access | full_access_as_app | Use Exchange Web Services with full access to all mailboxes |
Click the "Add permissions" button to save the configuration.
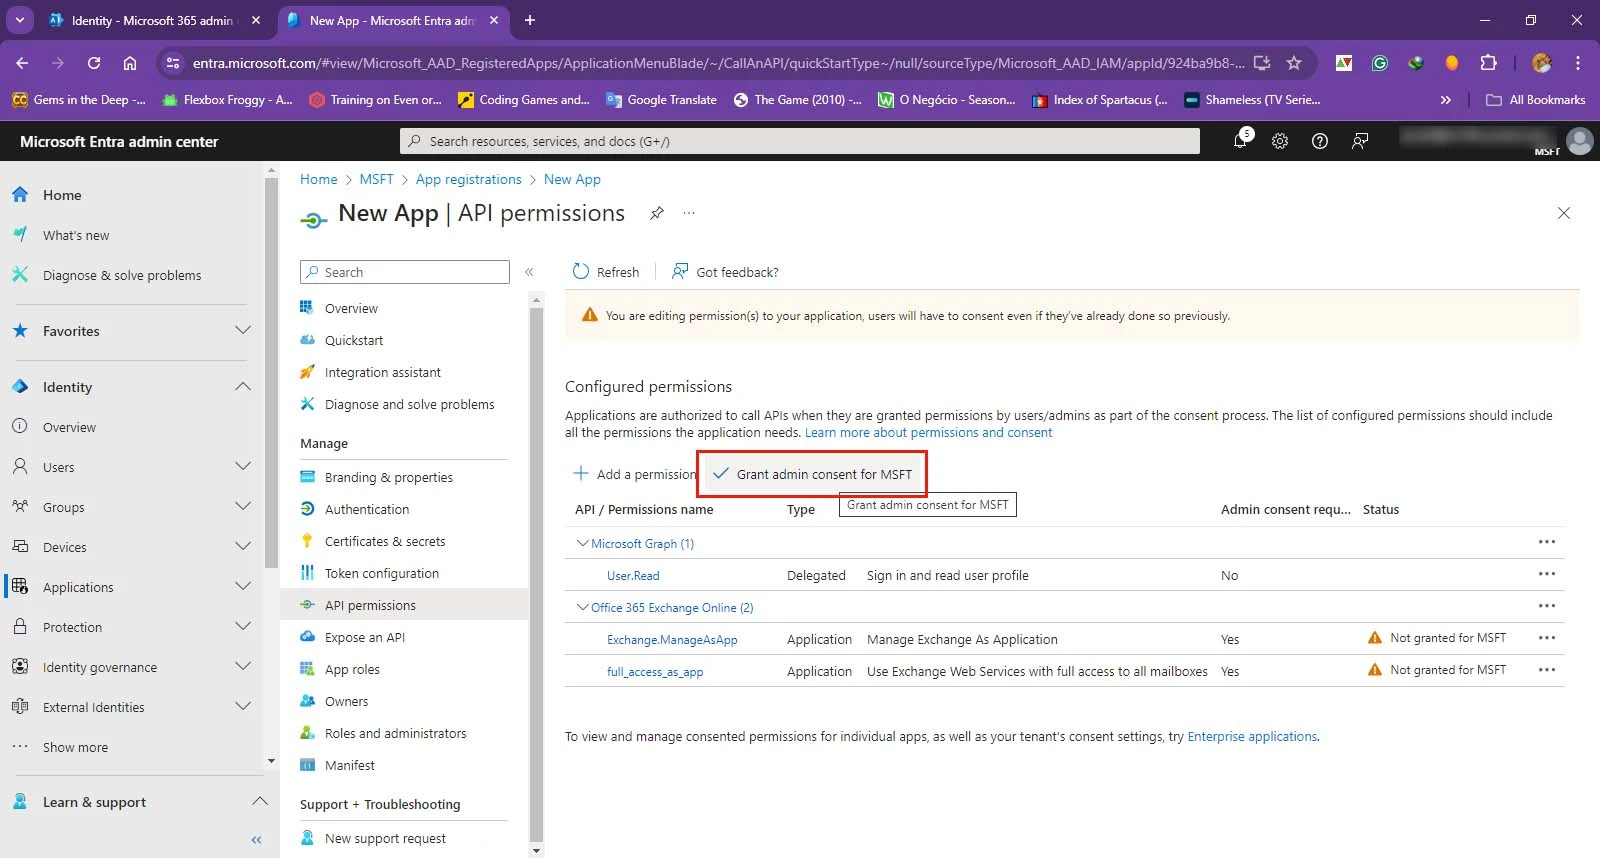
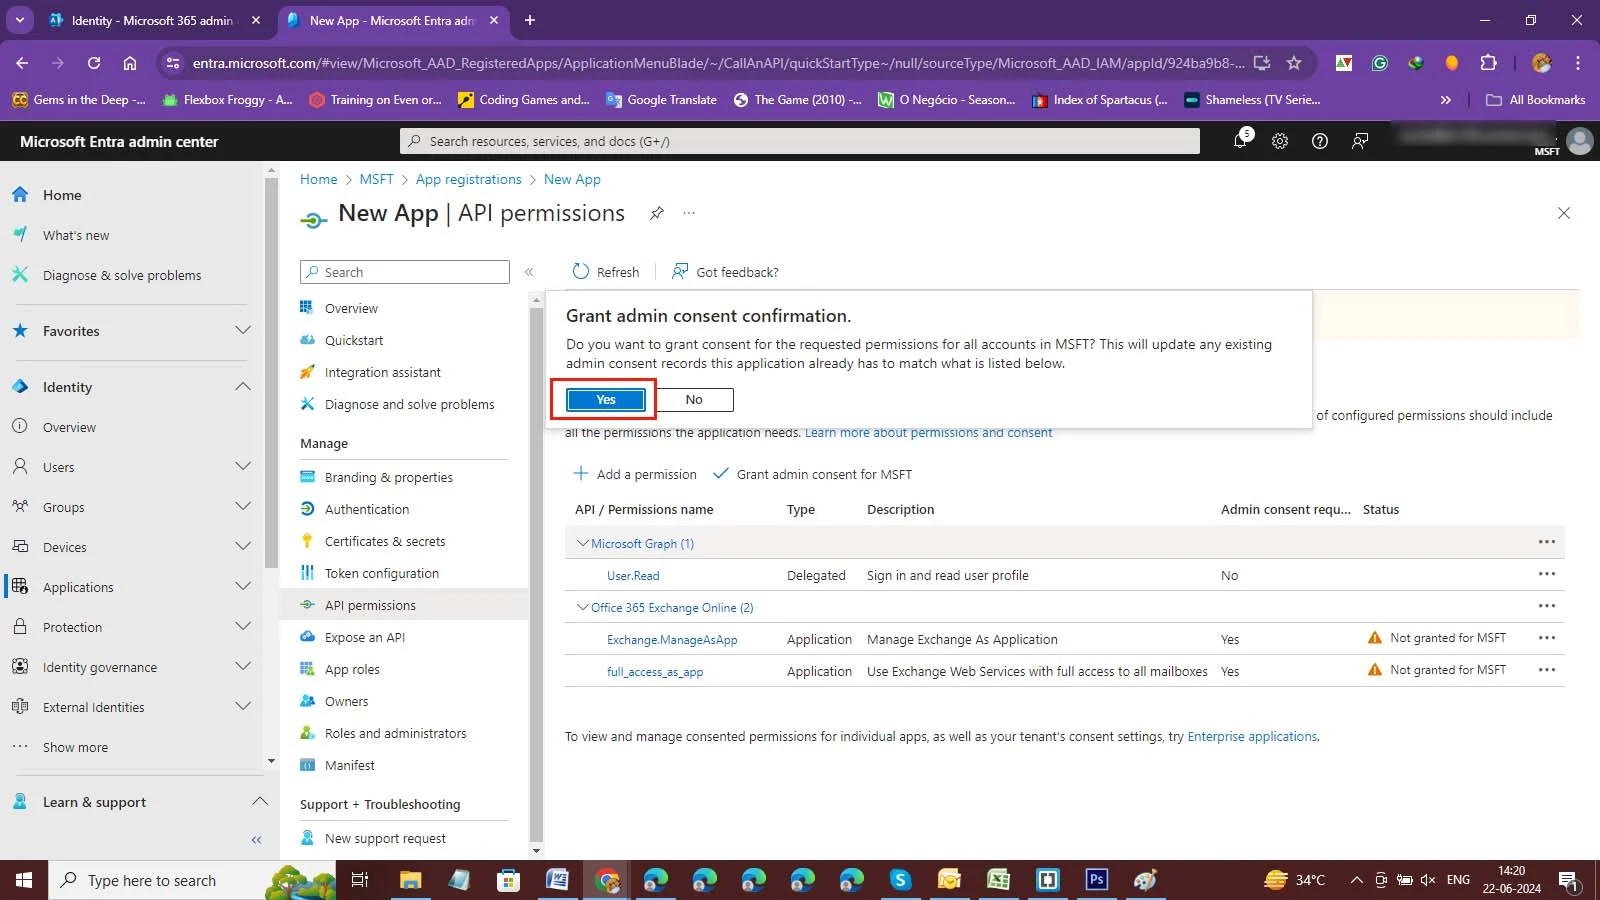
After adding the permissions, they remain in an ungranted state until authorized. Under Configured permissions, click on "Grant admin consent for <Your Organization>".
A confirmation dialog appears. Click "Yes" to confirm admin consent. You will see green checkmarks under the Status column for all granted permissions.
Microsoft Graph Permissions (Teams, OneDrive, SharePoint)
Configure Microsoft Graph scopes for backing up and migrating Microsoft Teams channels, chats, OneDrive files, and SharePoint document libraries.
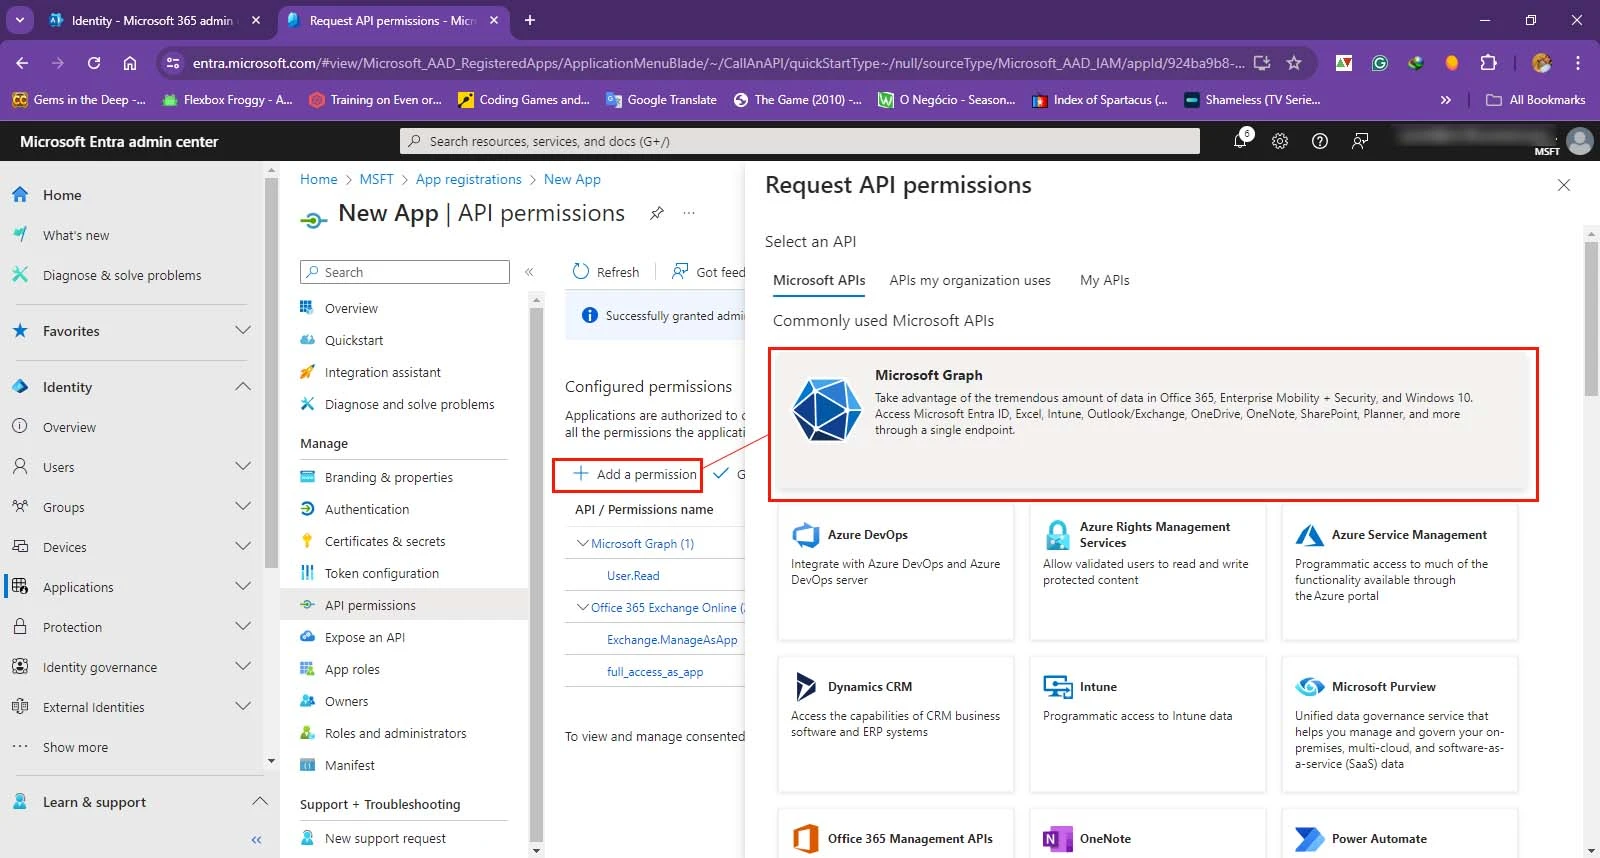
Click "+ Add a permission" again, and select "Microsoft Graph" under Microsoft APIs.
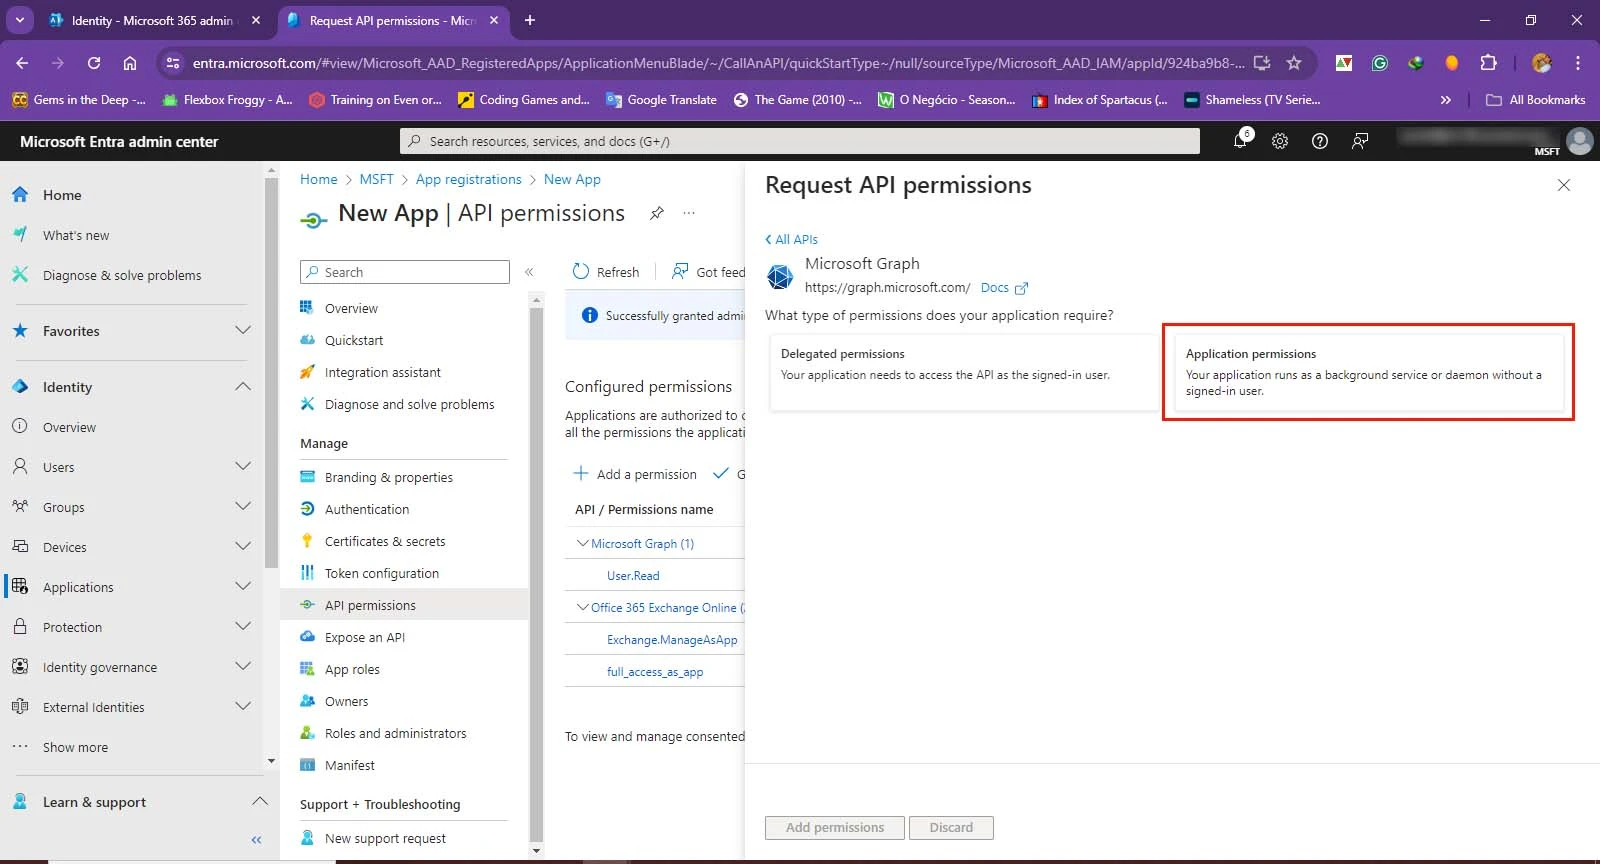
Select "Application permissions" to allow background synchronization without individual end-user prompts.
Complete Microsoft Graph Permission Reference Matrix
Depending on your migration scope (source vs. target), check the respective permissions from the table below:
| Category | Source Read Permissions | Target Write / Migration Permissions |
|---|---|---|
| Application | Application.Read.All | Application.ReadWrite.All, Application.ReadWrite.OwnedBy |
| Calendars | Calendars.Read, Calendars.ReadBasic.All | Calendars.ReadWrite |
| ChannelMessage | ChannelMessage.Read.All | N/A |
| Chat | Chat.Read.All | Chat.ReadWrite.All |
| Directory | Directory.Read.All | Directory.ReadWrite.All |
| Files | Files.Read.All | Files.ReadWrite.All |
| Group | Group.Read.All | Group.Create, Group.ReadWrite.All |
| GroupMember | GroupMember.Read.All | GroupMember.ReadWrite.All |
| Notes | Notes.Read.All | Notes.ReadWrite.All |
| Sites | Sites.Read.All | Sites.ReadWrite.All |
| Tasks | Tasks.Read.All | Tasks.ReadWrite.All |
| Team | Team.ReadBasic.All | Team.Create, Team.ReadBasic.All |
| TeamMember | TeamMember.Read.All, TeamMember.ReadWriteNonOwnerRole.All | TeamMember.ReadWrite.All, TeamMember.ReadWriteNonOwnerRole.All |
| TeamSettings | TeamSettings.Read.All | TeamSettings.ReadWrite.All |
| TeamsTab | TeamsTab.Read.All | TeamsTab.Create, TeamsTab.ReadWrite.All |
| TeamWork | N/A | Teamwork.Migrate.All |
| TeamworkApp | TeamworkAppSettings.Read | TeamworkAppSettings.Read |
| TeamworkAppSettings | TeamworkAppSettings.Read.All | TeamworkAppSettings.ReadWrite.All |
| TeamworkTag | TeamworkTag.Read.All | TeamworkTag.ReadWrite.All |
| User | User.Read, User.Read.All | User.Read |
Generate Client Secret Value
The Client Secret acts as the password for your application when authenticating via OAuth2.
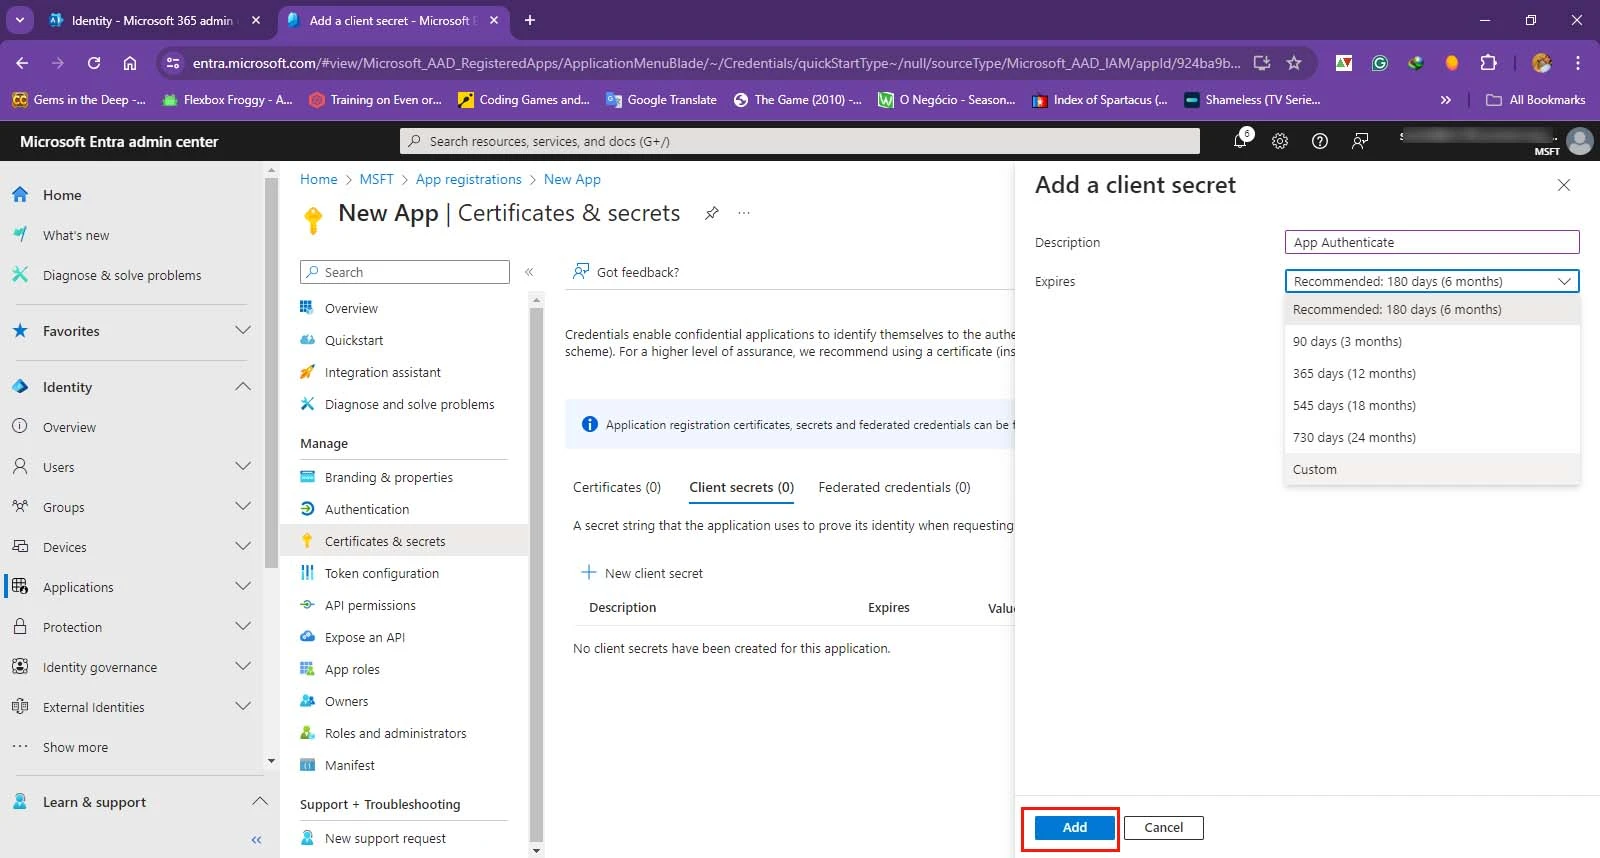
From the left-hand Manage menu, select "Certificates & secrets". On the Client secrets tab, click on "+ New client secret".
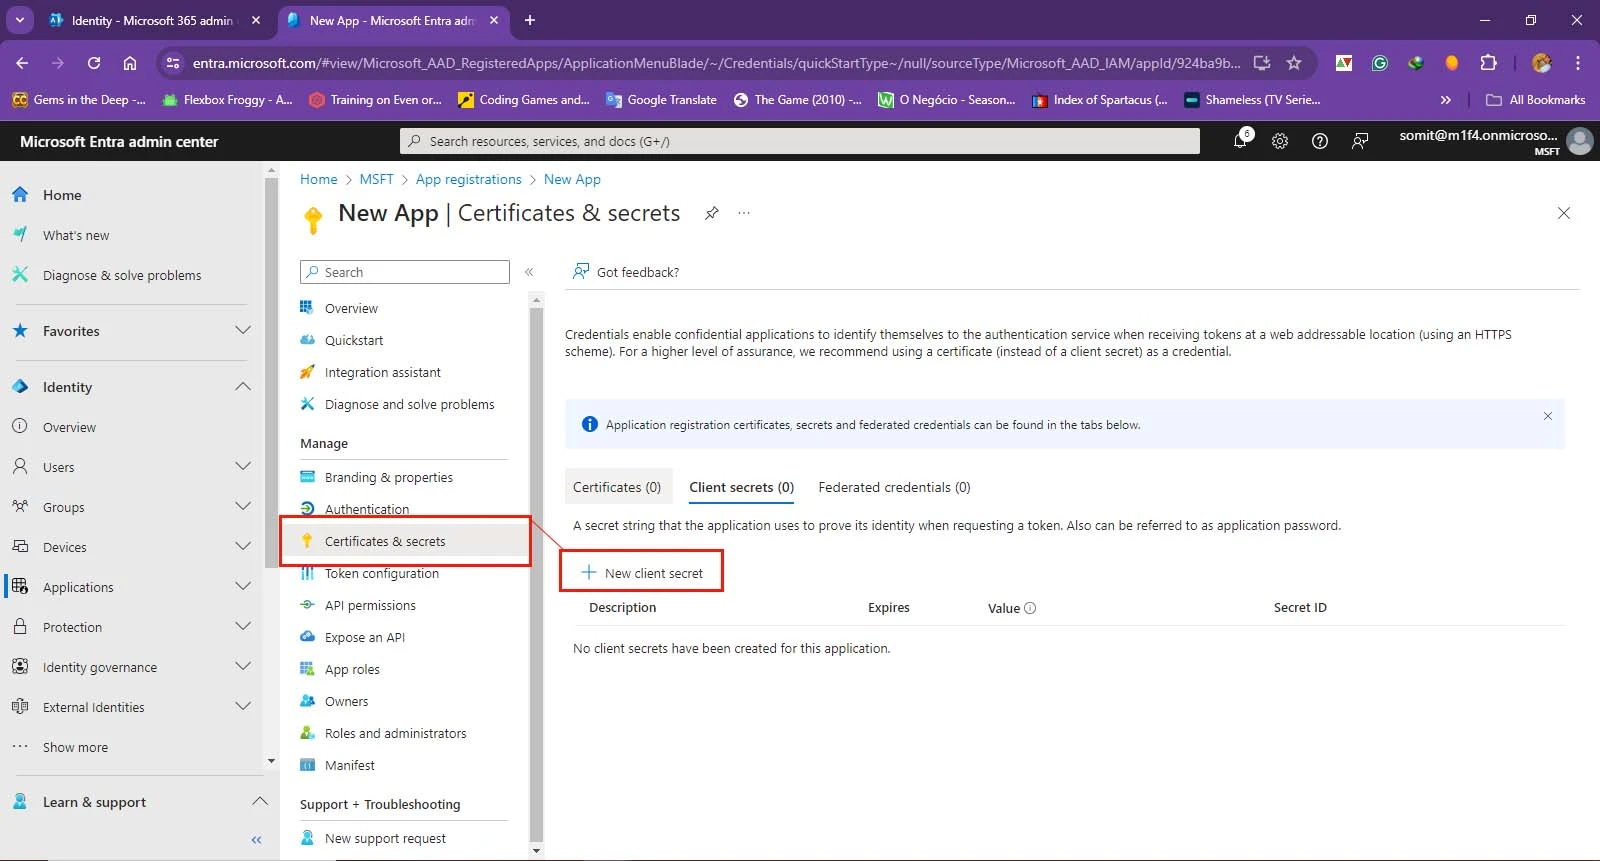
Provide a short description (e.g. MailsDaddySecret) and select your desired expiration timeframe (such as 180 days or 24 months). Then click "Add".
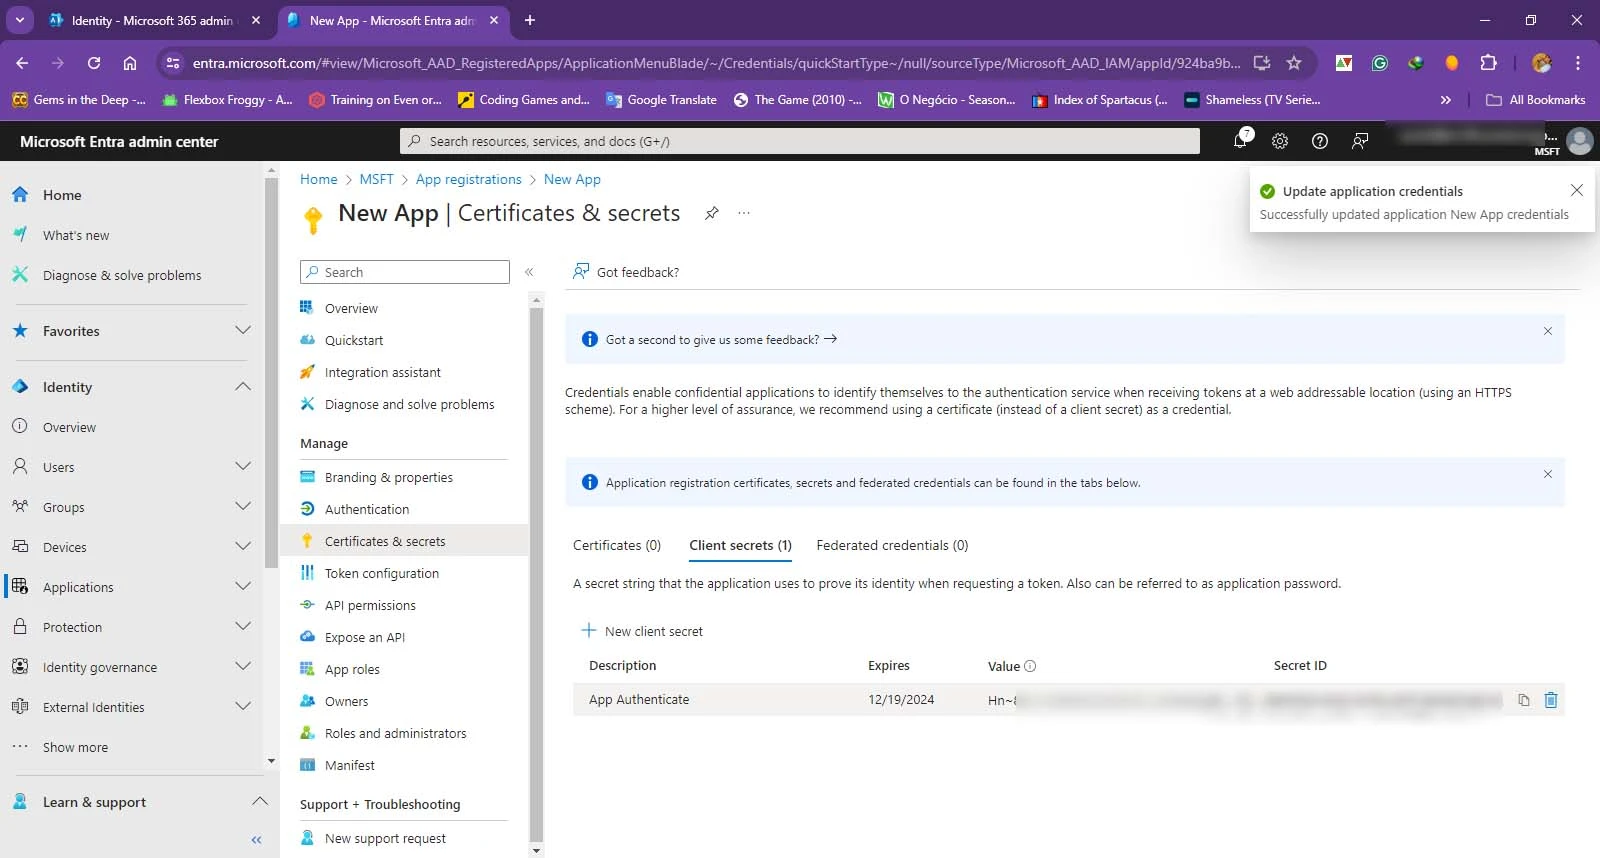
Azure displays the secret in the table. Copy the text from the "Value"column (NOT the "Secret ID" column) and save it in a secure location.
Assign Global Administrator Role
Required for cross-mailbox migration and tenant-wide mailbox mapping in MailsDaddy migration software.
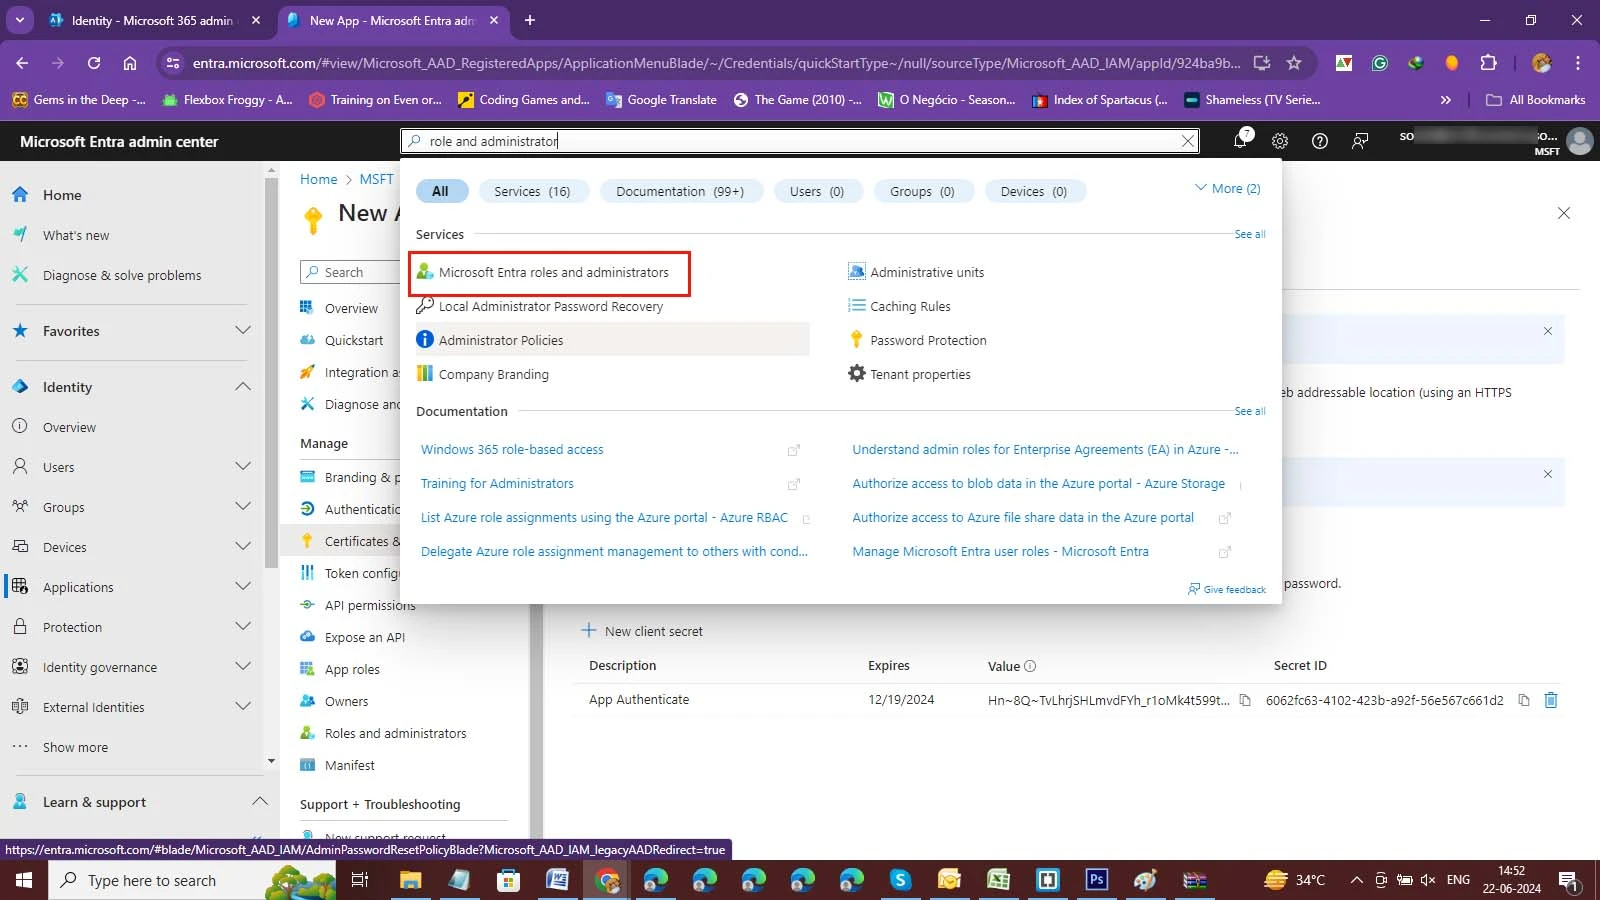
In the top search bar of Microsoft Entra ID, type "roles and administrators" and select it from the search results.
Type "Global Administrator" in the role search box, and click on the Global Administrator role to open it.
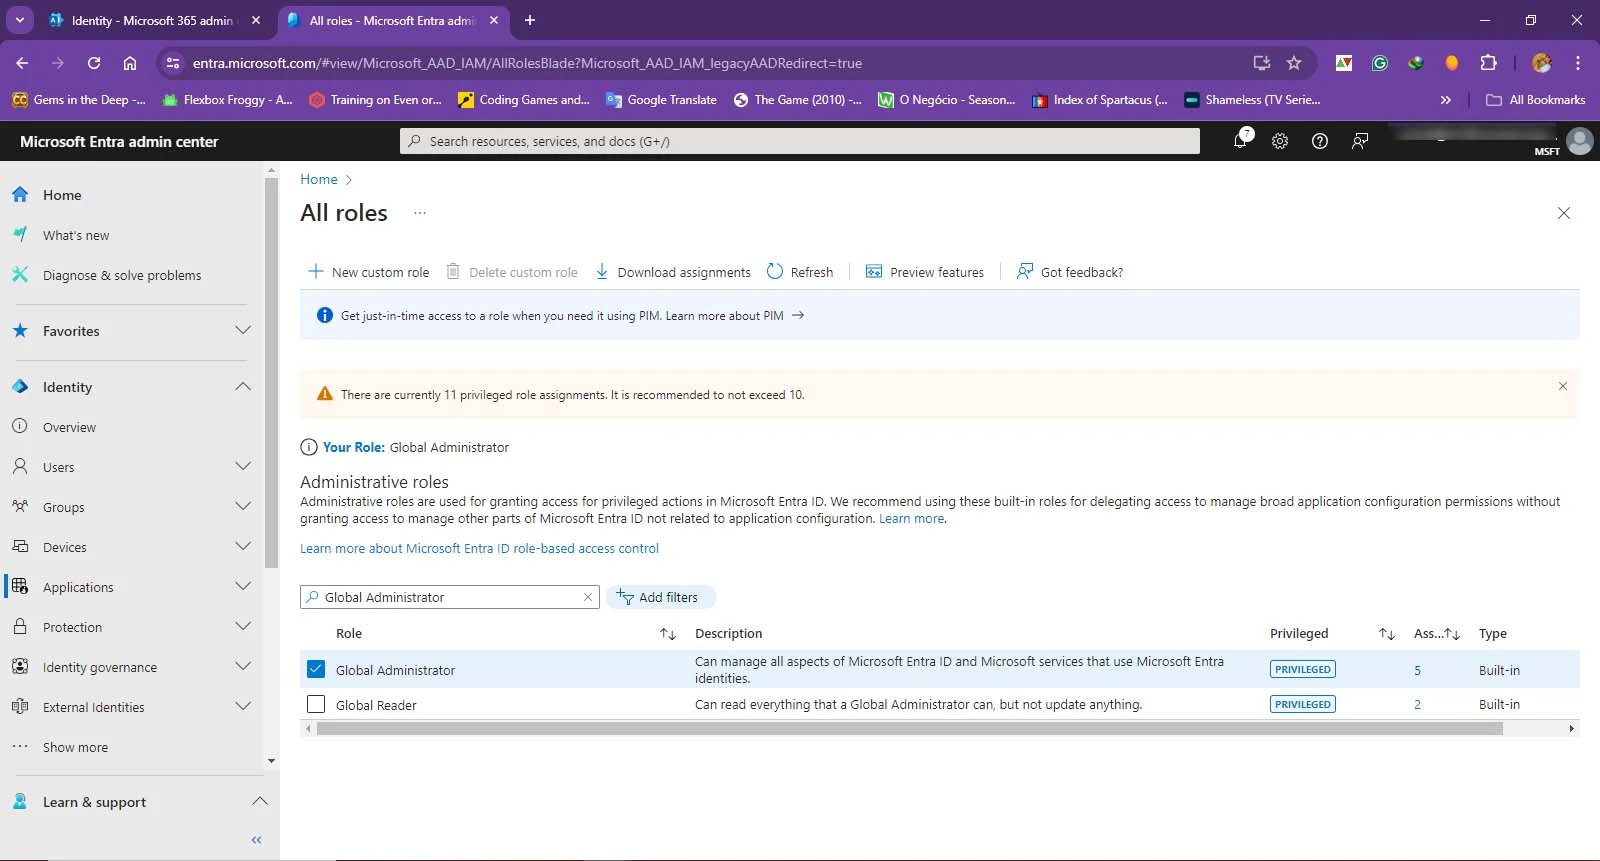
On the top action bar of the Global Administrator role page, click the "+ Add assignments" button.
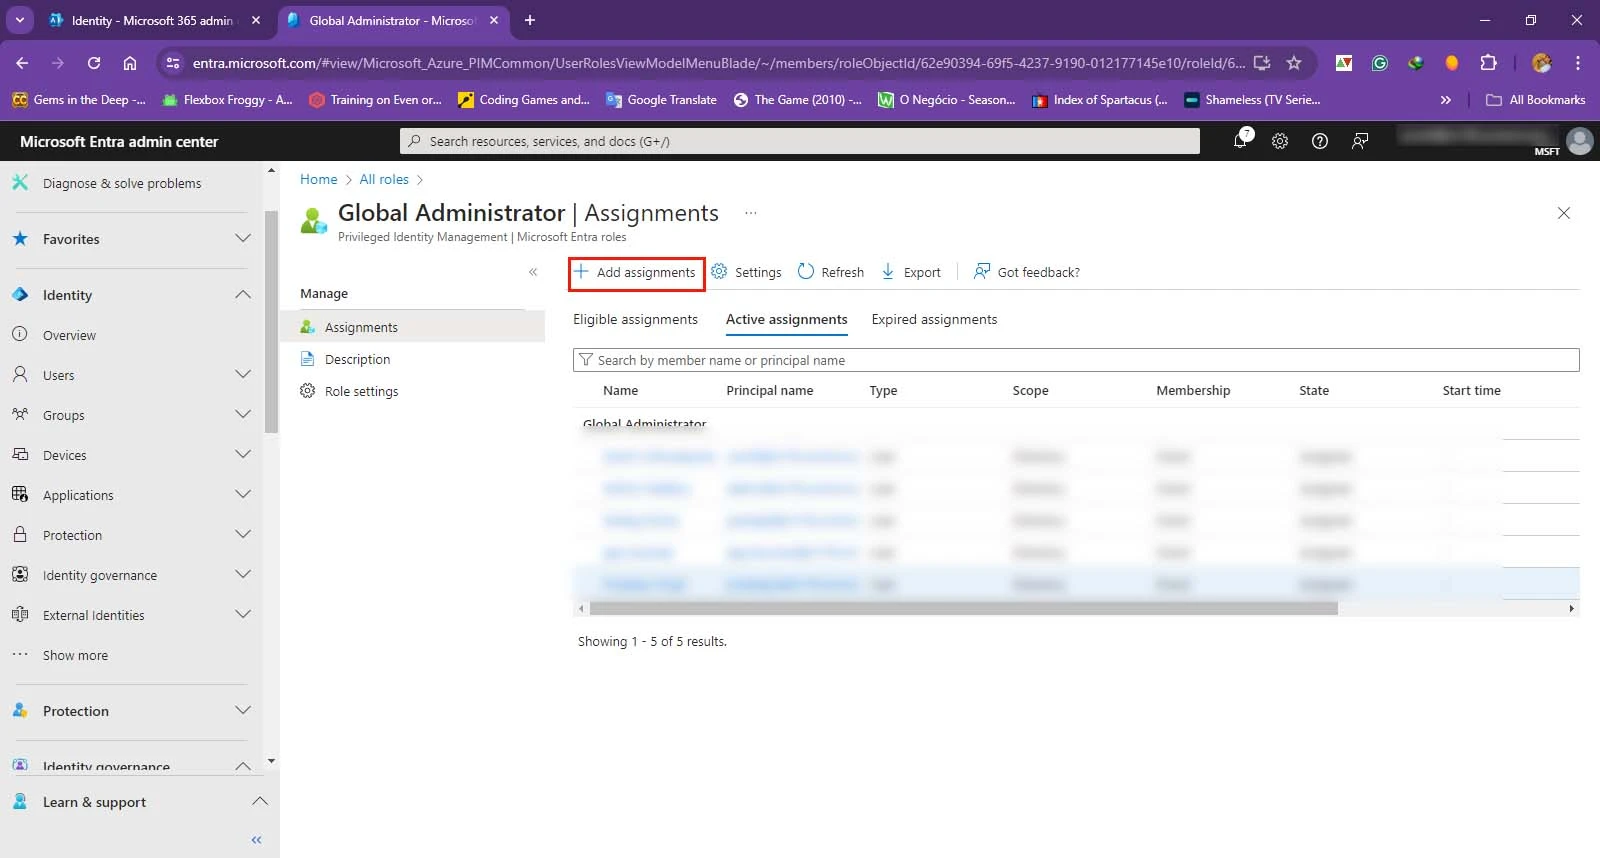
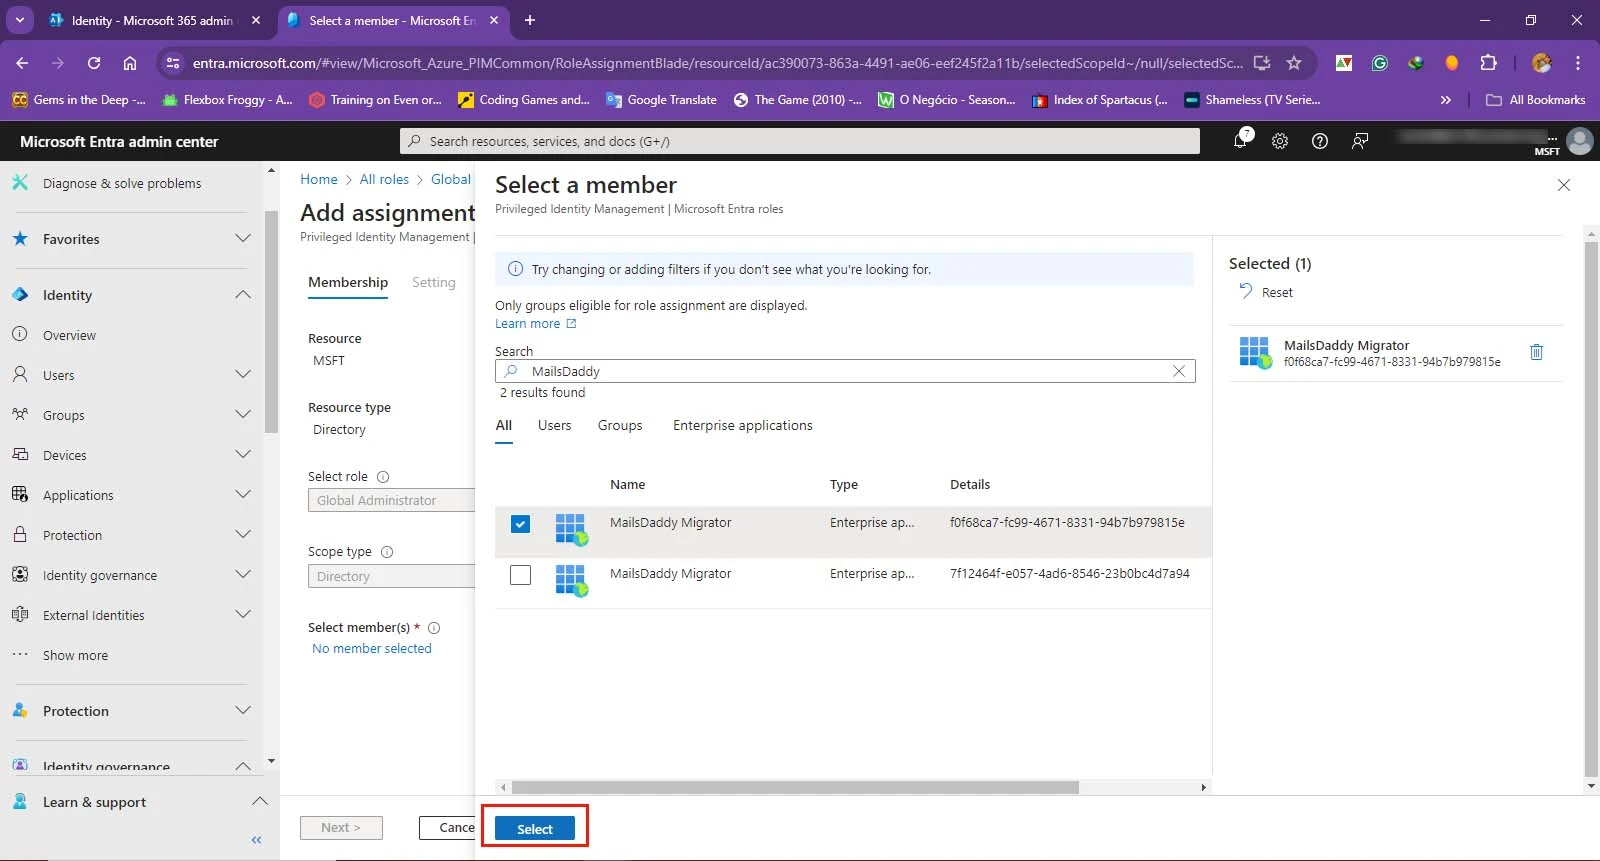
Type the name of your registered application (e.g. MailsDaddy Migration App) in the search field. Select the checkbox next to it, and click the "Add" button.
Where to Find Tenant ID, Client ID & Secret?
Read our dedicated companion tutorial showing exactly where to copy your Directory (Tenant) ID, Application (Client) ID, and paste them into MailsDaddy software.