How to Get Tenant ID, Client ID & Secret Value in Azure AD
To connect MailsDaddy Office 365 Backup, Exchange Migration, or Cloud Migration software via Modern Authentication, you need three key credentials from Microsoft Entra ID (Azure AD). Follow these illustrated steps to create your Azure app, generate the client secret, and grant the required mailbox permissions.
Directory (Tenant) ID
Identifies your Microsoft 365 tenant domain.
Application (Client) ID
Unique GUID assigned to your registered app.
Client Secret Value
OAuth2 authorization token created in Certificates & secrets.
Create & Register a New App in Azure AD
Access the Azure portal to create your application entry and obtain your Client ID and Tenant ID.
Sign into Microsoft 365 Admin Center & Navigate to App Registrations
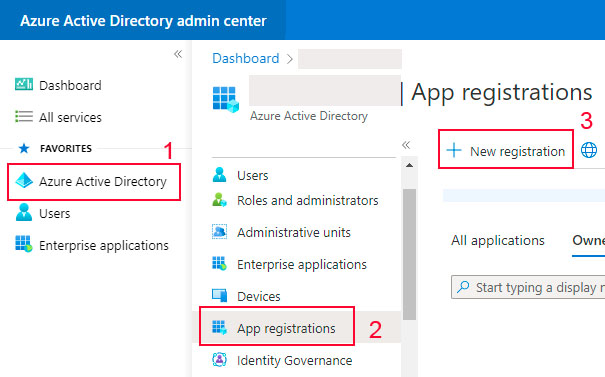
Sign in to the Microsoft 365 Admin Center with administrator credentials and open the Azure Active Directory admin center (or portal.azure.com). Under the App registrations section, click "New registration".
Configure Application Name & Register
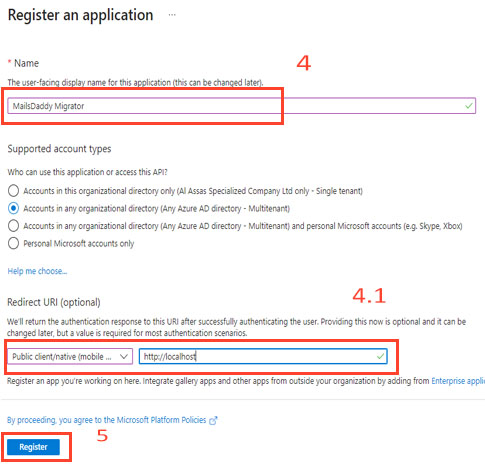
Enter your desired application name (e.g. MailsDaddy Migration), select who can use this application or access the API (Single Tenant: Accounts in this organizational directory only), specify a Redirect URI if requested, and then click the "Register" button.
Copy Application (Client) ID and Directory (Tenant) ID
Your application is now registered! In the Overview section essentials panel, copy your Application (client) ID and Directory (tenant) ID and store them safely.
XXXXXXXX-XXXX-XXXX-XXXX-XXXXXXXXXXXXXXXXXXXX-XXXX-XXXX-XXXX-XXXXXXXXXXXX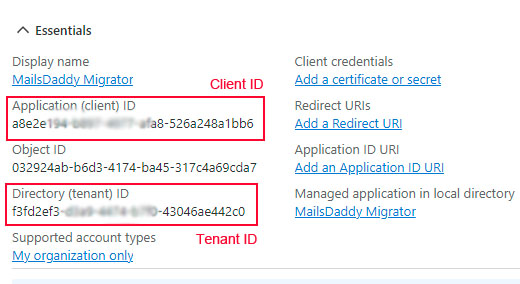
Create & Configure Client Secrets
Generate the authentication secret that will be paired with your Client ID.
Open "Certificates & secrets" → Click "+ New client secret"
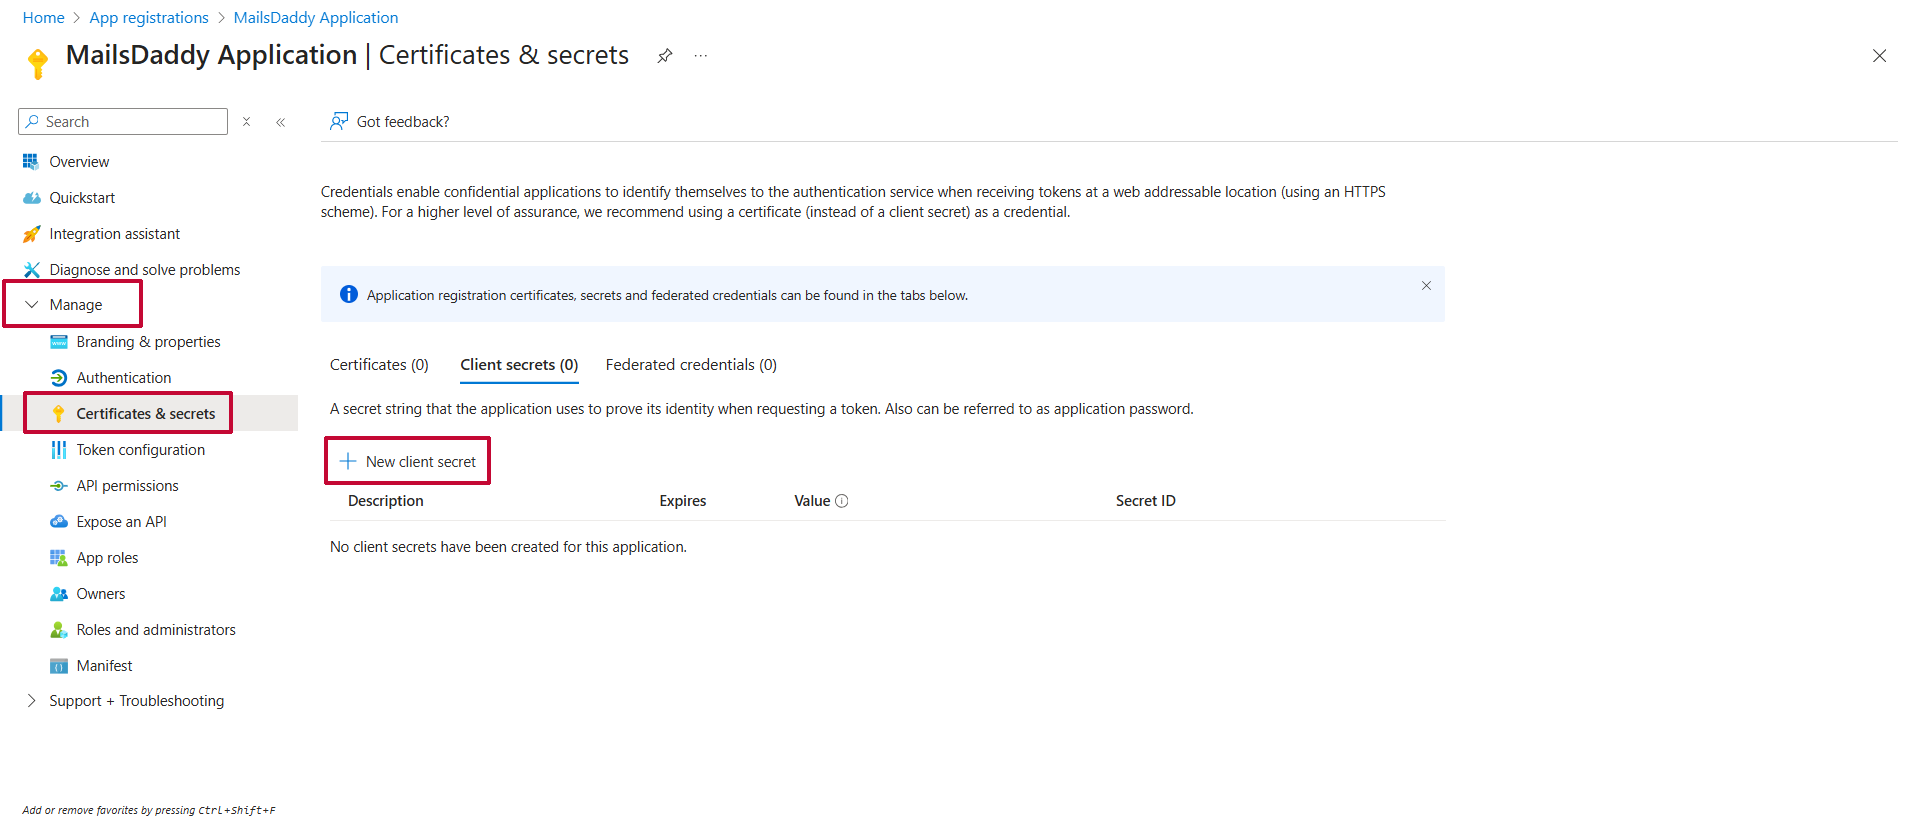
In the left-hand navigation menu under Manage, click on "Certificates & secrets", then click on the "+ New client secret" button under the Client secrets tab.
Enter Description & Expiration Duration
Type a Description (e.g. MailsDaddy Secret), select the preferred expire period (such as 180 days or 24 months), and click the "Add" button.
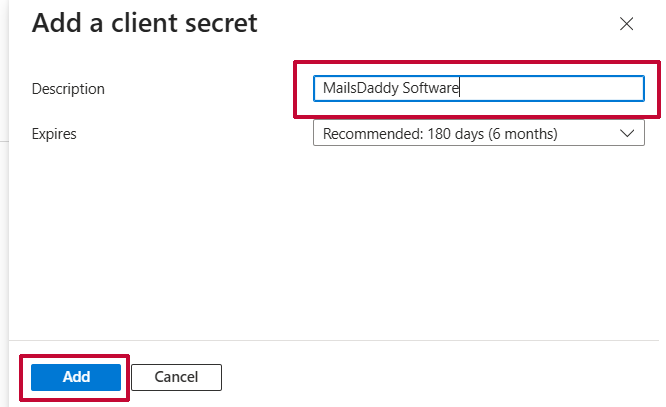
Copy the Client Secret Value (Crucial Step)
The new secret will now appear in the Client secrets table. Copy the string in the "Value" column immediately.

Grant Required API Permissions
Authorize the application to access and export/import mailboxes, contacts, calendars, tasks, and notes.
Step 3A: Add Microsoft Graph Application Permissions
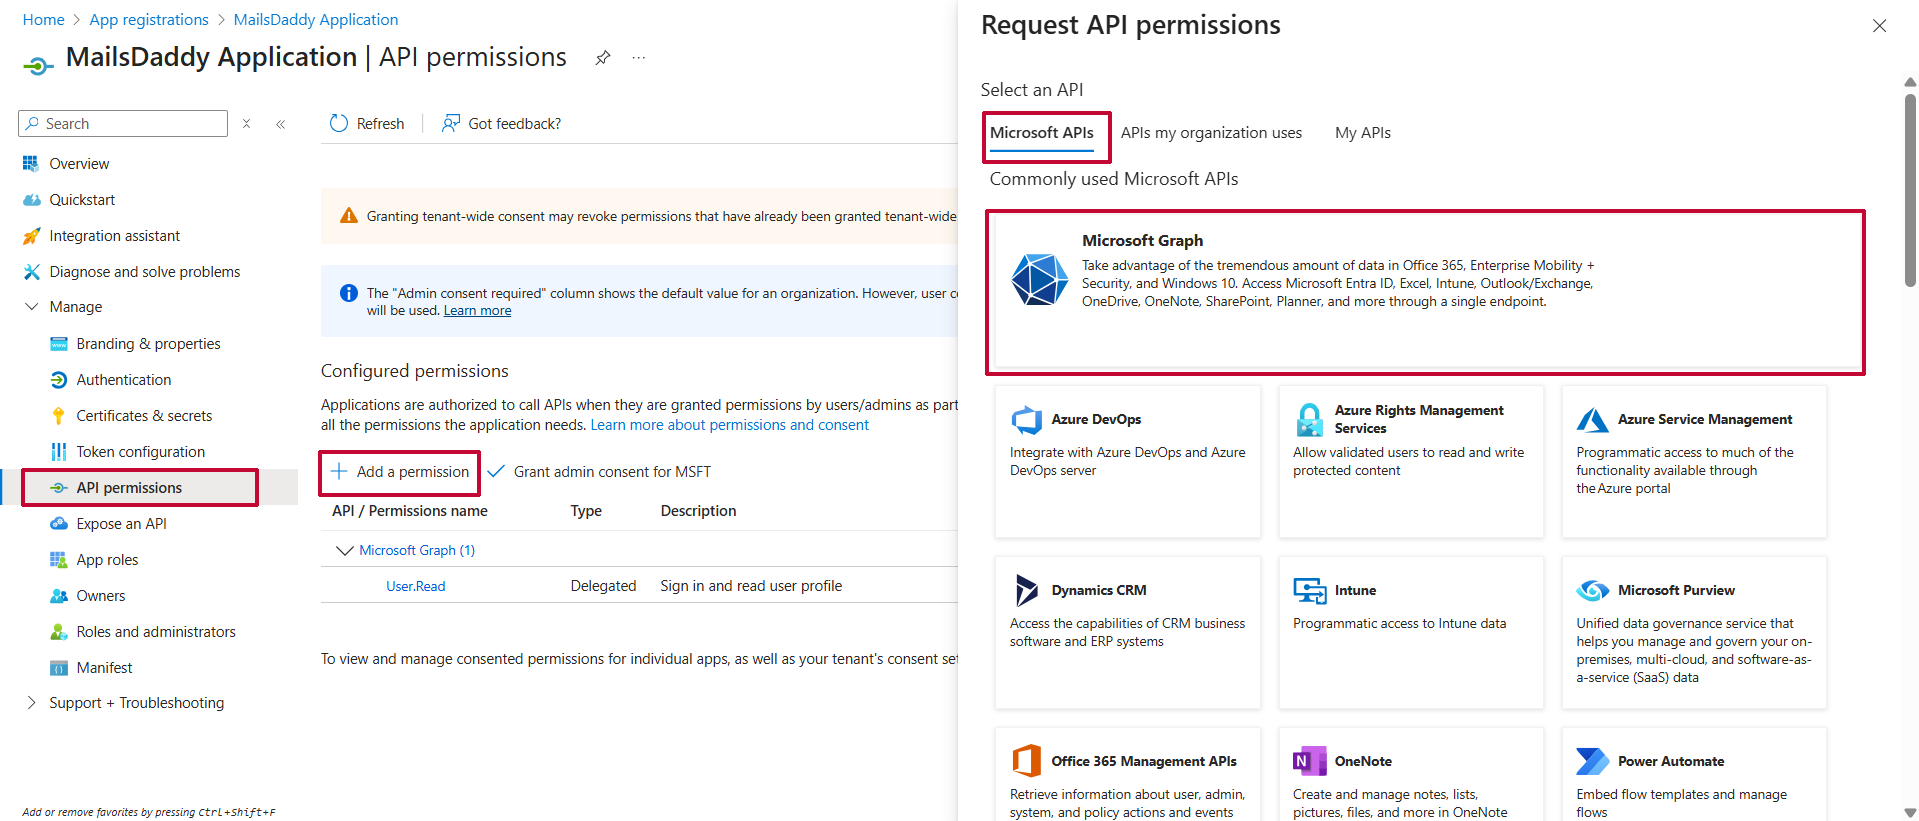
Click on the "API permissions" option in the left menu, then click "+ Add a permission". Select "Microsoft Graph" from the Microsoft APIs list.
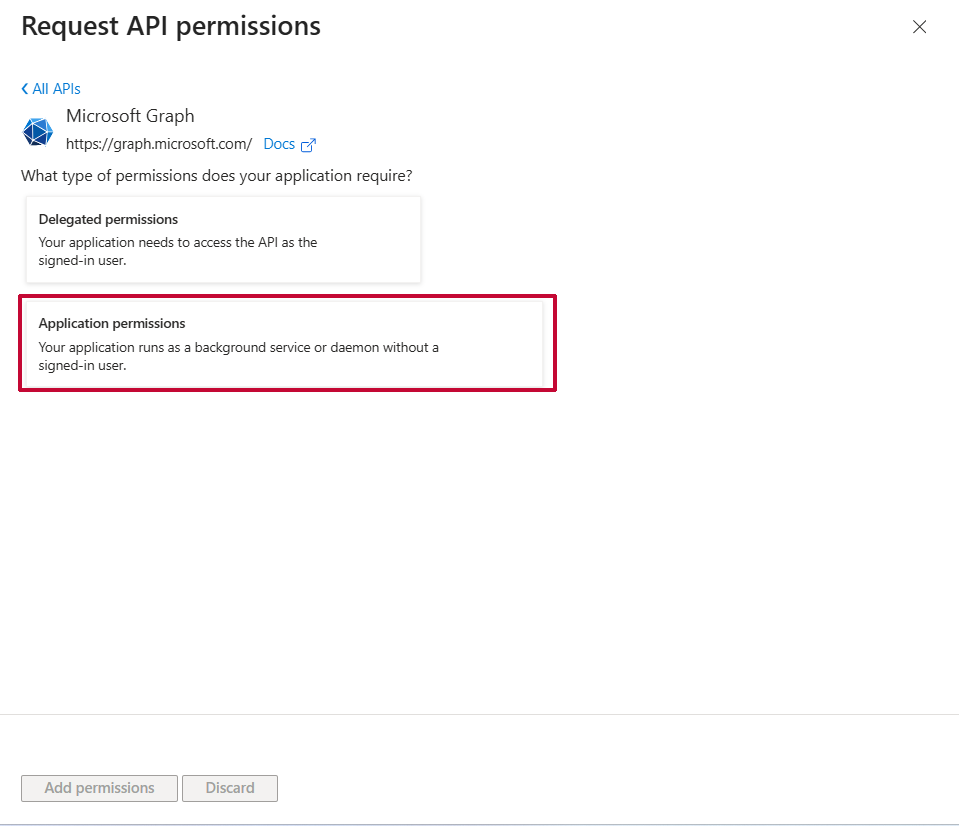
Click on "Application permissions":
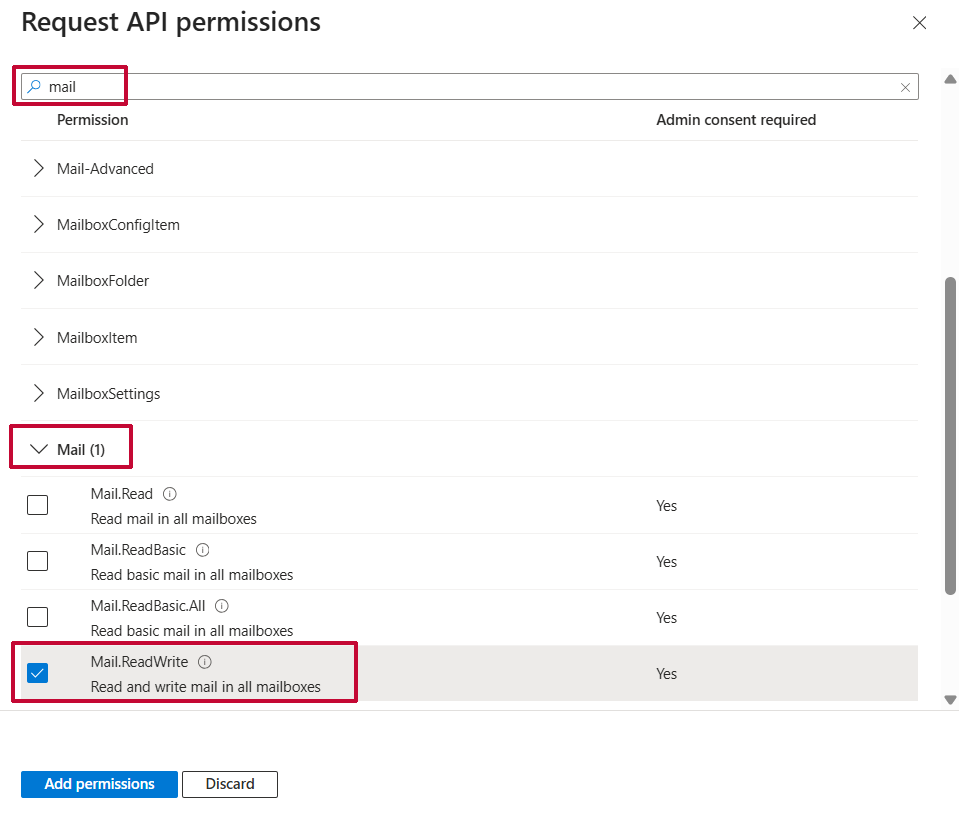
Now search and enable the required scopes for each mailbox item:
Search for "Mail" and check Mail.ReadWrite.
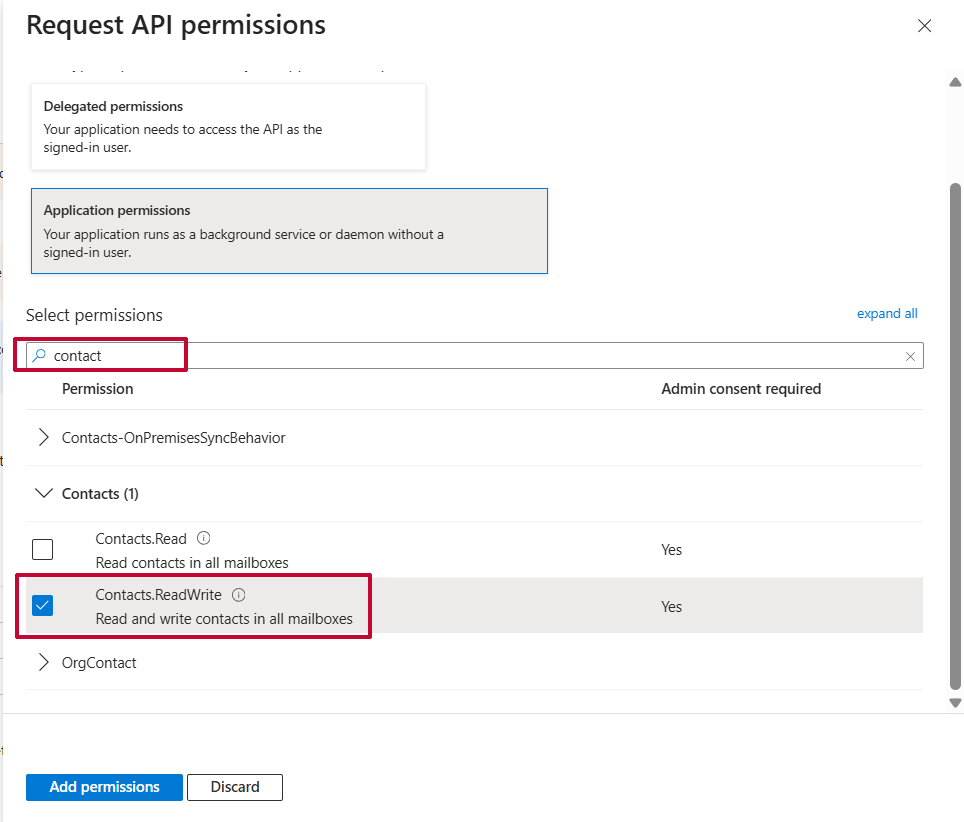
Search for "Contact" and check Contacts.ReadWrite.
Search for "Calendar" and check Calendars.ReadWrite.

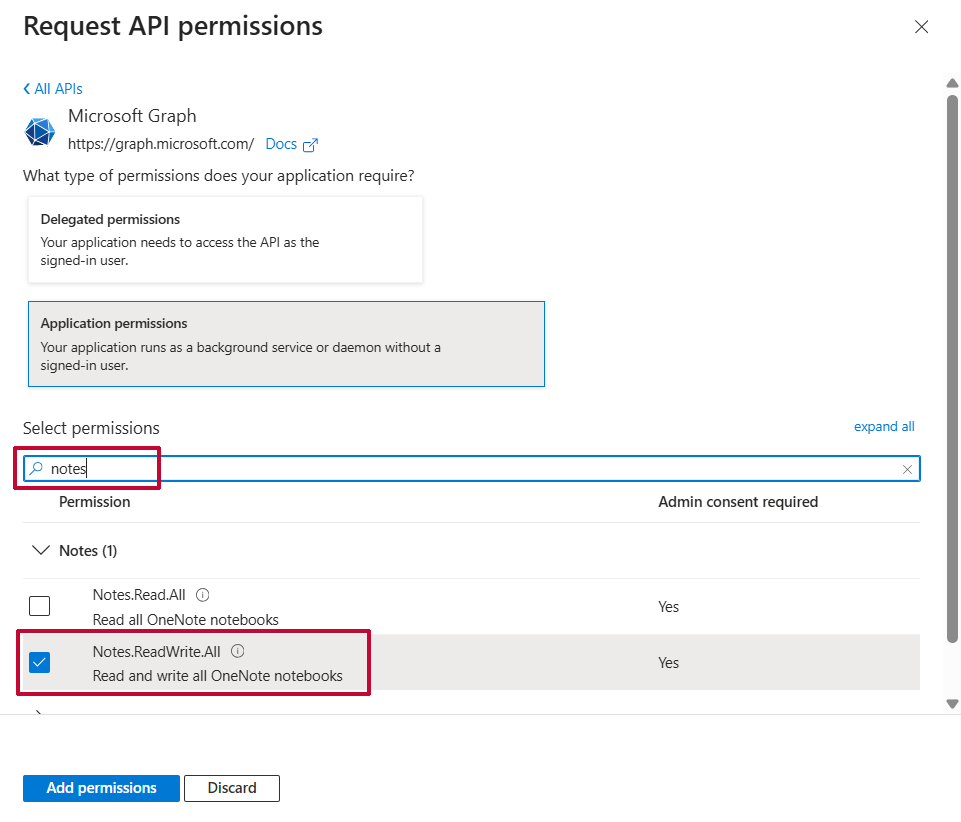
Search for "Notes" and check Notes.ReadWrite.All.
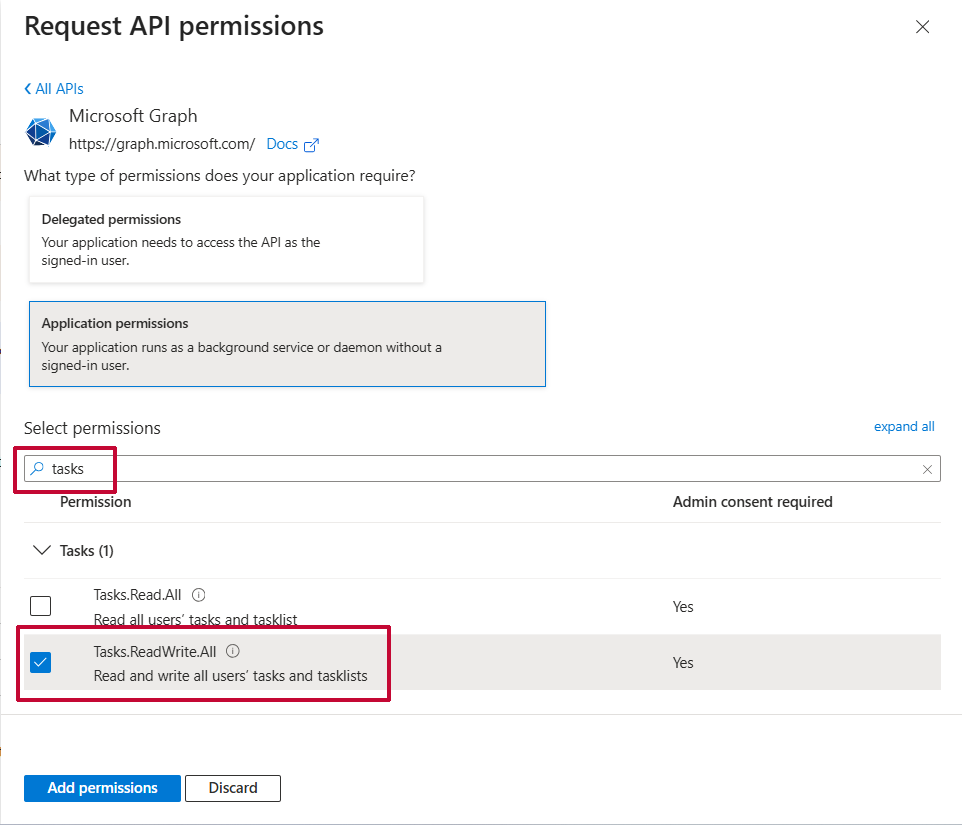
Search for "Tasks" and check Tasks.ReadWrite.
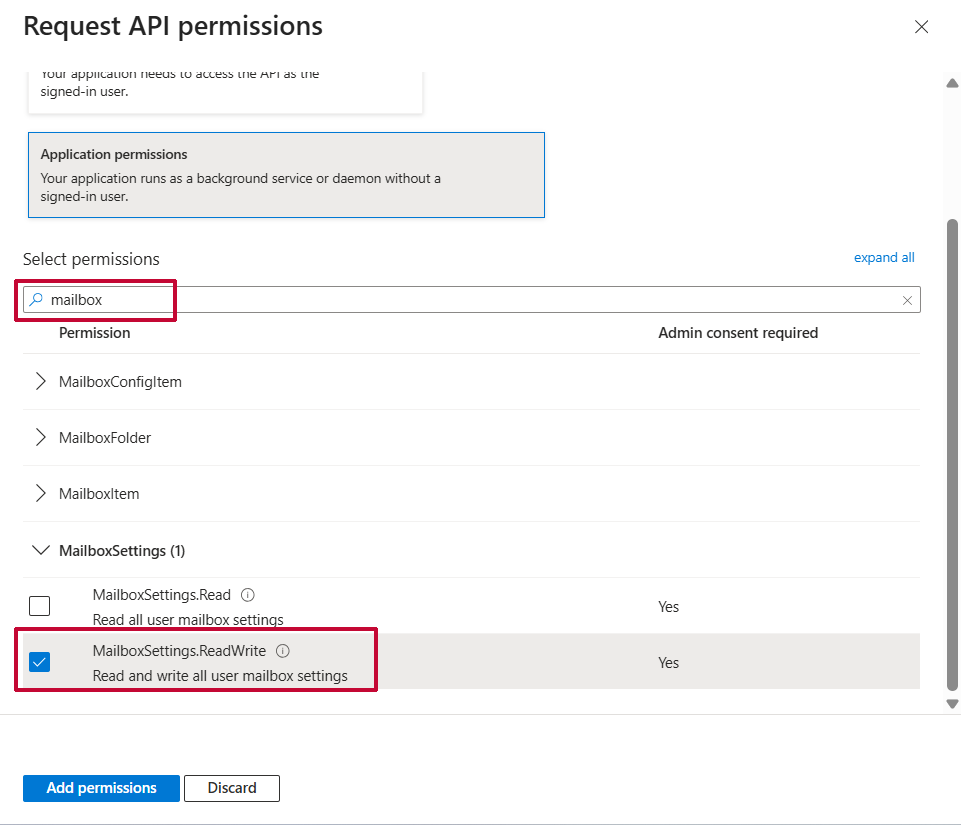
Search for "Mailbox settings" and enable ReadWrite.
Search for "User" and enable User.Read.All.
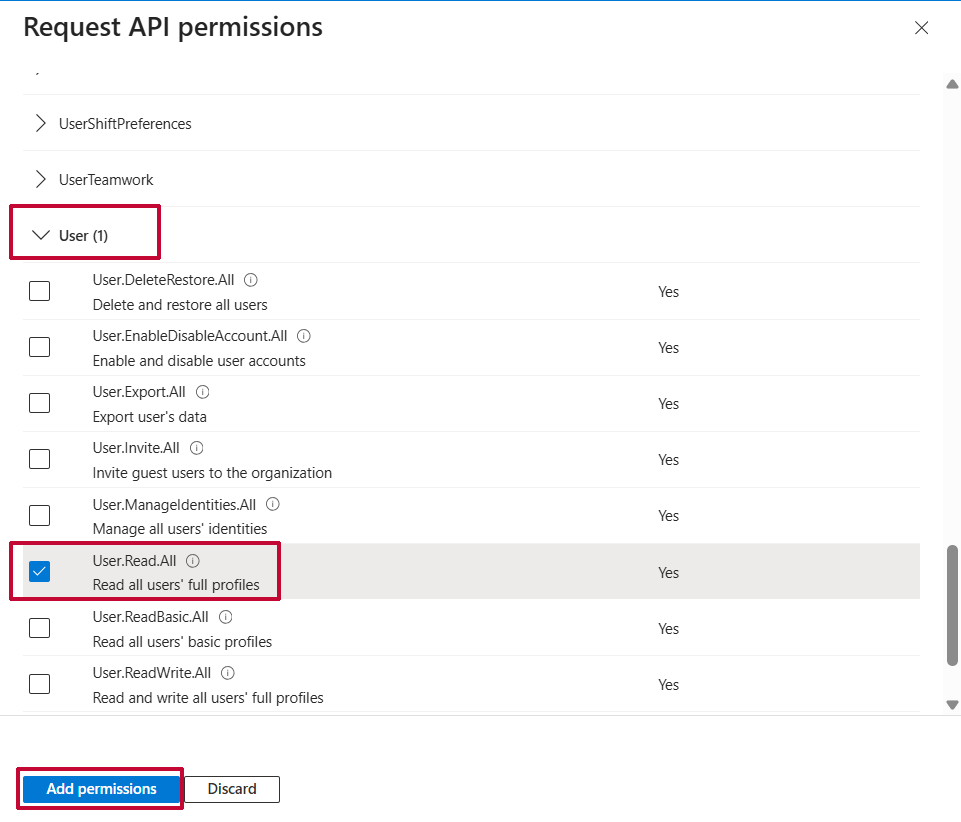
Once all permissions are selected, click the "Add Permissions" button.
Step 3B: Add Office 365 Exchange Online Permissions
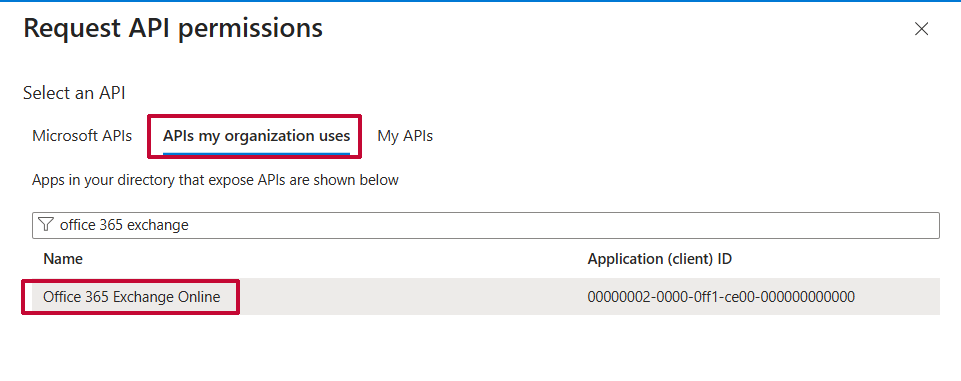
Now click "Add a permission" again. Select the "APIs my organization uses" tab and search for Office 365 Exchange Online. Click on it from the list.
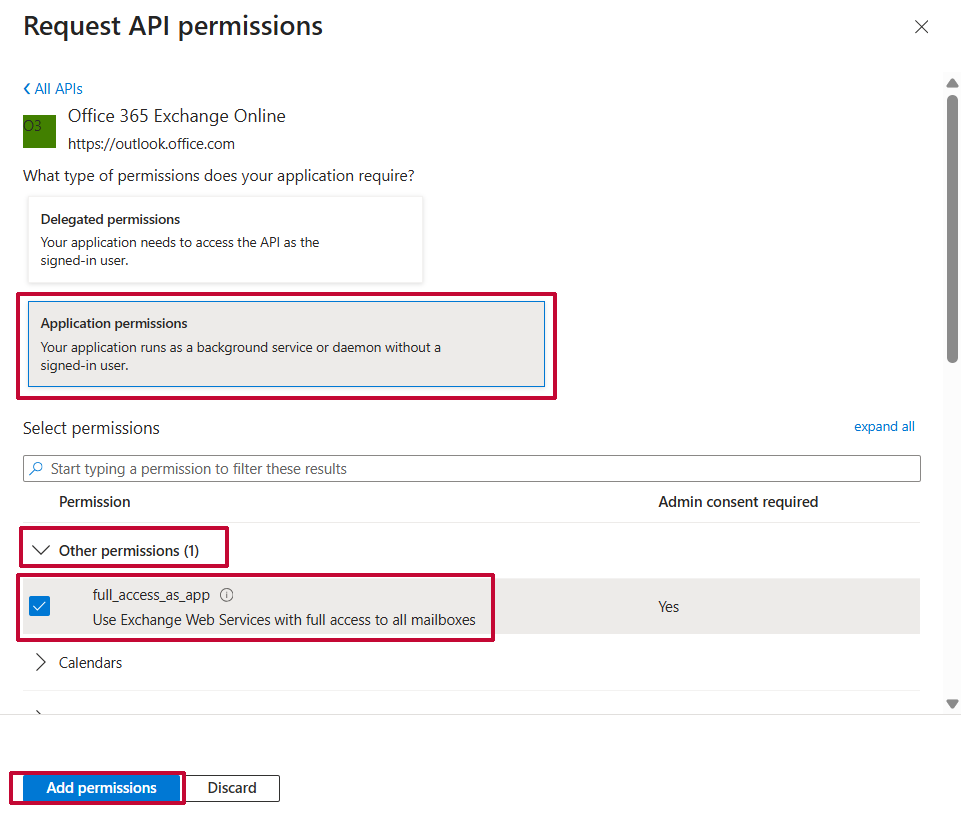
Select Application permissions, check full_access_as_app, and click the "Add permissions" button.
Step 3C: Grant Admin Consent
To activate all permissions, click the "Grant admin consent for <Your Organization>" button on the API permissions page.
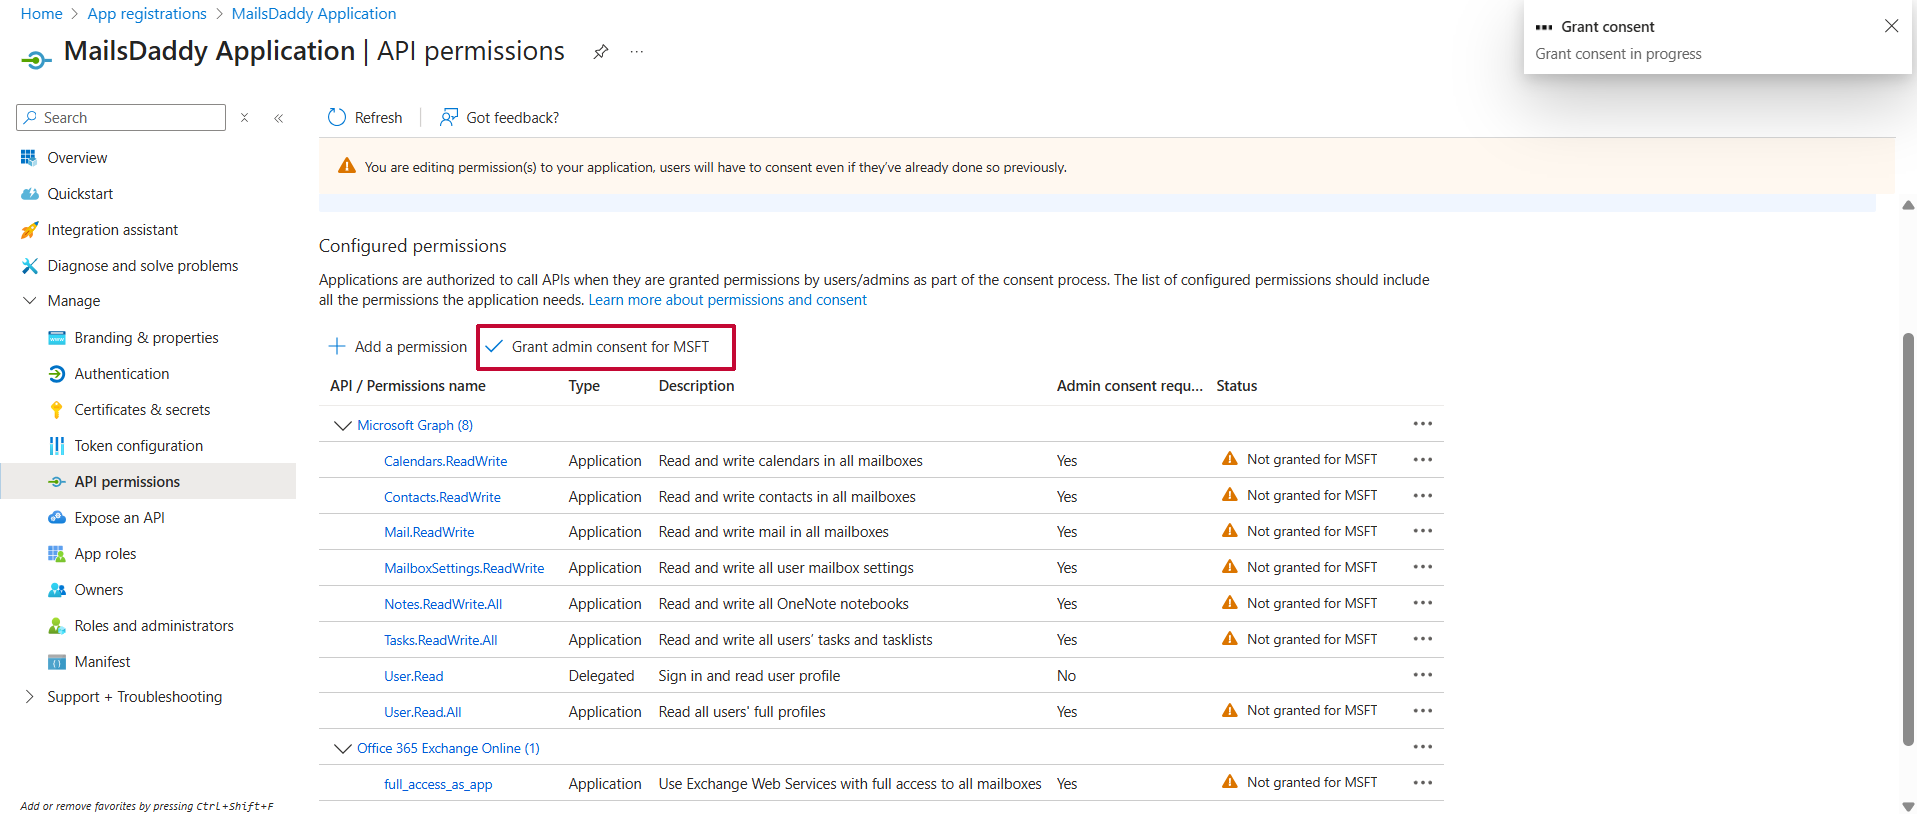
A confirmation dialog "Grant admin consent confirmation" will appear. Click "Yes".

All Done! How to Use Credentials in MailsDaddy Software
Connecting your Microsoft 365 tenant using Modern Authentication
Launch your MailsDaddy software (such as MailsDaddy Office 365 Backup, Exchange Server Migration, or Cloud Migration Tool). On the Sign-in dialog, choose "Modern Authentication" and paste your credentials:
Paste your Application (client) ID
Paste your Directory (tenant) ID
Paste your Client Secret Value
Enter your Microsoft 365 Admin email and click Sign In. The application will connect securely via OAuth 2.0 without triggering legacy basic auth blocks.